Cyber, data privacy and AI governance, evidenced.
FalconryTrust connects cyber risk, privacy obligations, AI governance, controls, evidence, third parties, issues and assurance in one governed environment—so security and privacy leaders can demonstrate not only what is required, but what is actually working.
Security, privacy and AI governance fail when each discipline builds its own evidence trail.
Leaders are expected to answer connected questions about exposure, regulatory obligations, control effectiveness, third parties and emerging technology. When those answers live across separate spreadsheets, tools and point-in-time assessments, confidence becomes difficult to demonstrate.
Risk is fragmented
Cyber, privacy, AI and third-party exposure are assessed separately even when they affect the same services and assets.
Controls are repeatedly mapped
Different frameworks and regulators create duplicate control and evidence work.
Evidence ages quickly
Compliance snapshots do not show whether controls continue to operate after the assessment ends.
Emerging AI use outpaces governance
AI inventories, risks, approvals and obligations can develop faster than oversight structures.
One trust record. Evidence behind every claim.
FalconryTrust connects obligations, risks, controls, assets, data, third parties, AI use cases, evidence, exceptions and remediation. The result is a governed line of sight from what the organisation must protect to how it proves control effectiveness and responds when exposure changes.
From obligation and asset to control evidence and assurance.
FalconryTrust turns security, privacy and AI governance requirements into accountable, testable and reportable operating records.
The model can also connect processing activities, third parties, AI use cases, incidents, vulnerabilities, policies, owners, assessments, tests and regulatory reporting.
Operate cyber, privacy and AI governance as connected trust disciplines.
Manage cyber risk
Connect threats, assets, vulnerabilities, controls, incidents and remediation to enterprise risk and ownership.
CYBER RISKGovern privacy
Structure obligations, processing activities, data, assessments, controls, rights and evidence in one privacy record.
DATA PRIVACYGovern AI use
Inventory AI use cases, classify risk, assign accountability, capture approvals and maintain control evidence.
AI GOVERNANCEAssess third parties
Evaluate vendor risk, criticality, evidence, issues and remediation against the services and data they support.
THIRD-PARTY TRUSTOperate controls & evidence
Reuse common controls across requirements and maintain evidence, testing and exception history over time.
CONTROL ASSURANCEReport trust posture
Give executives and committees a connected view of exposure, compliance, control health and unresolved action.
EXECUTIVE REPORTINGSee cyber, privacy and AI governance through one operating environment.
These views illustrate common working contexts across the proposition.
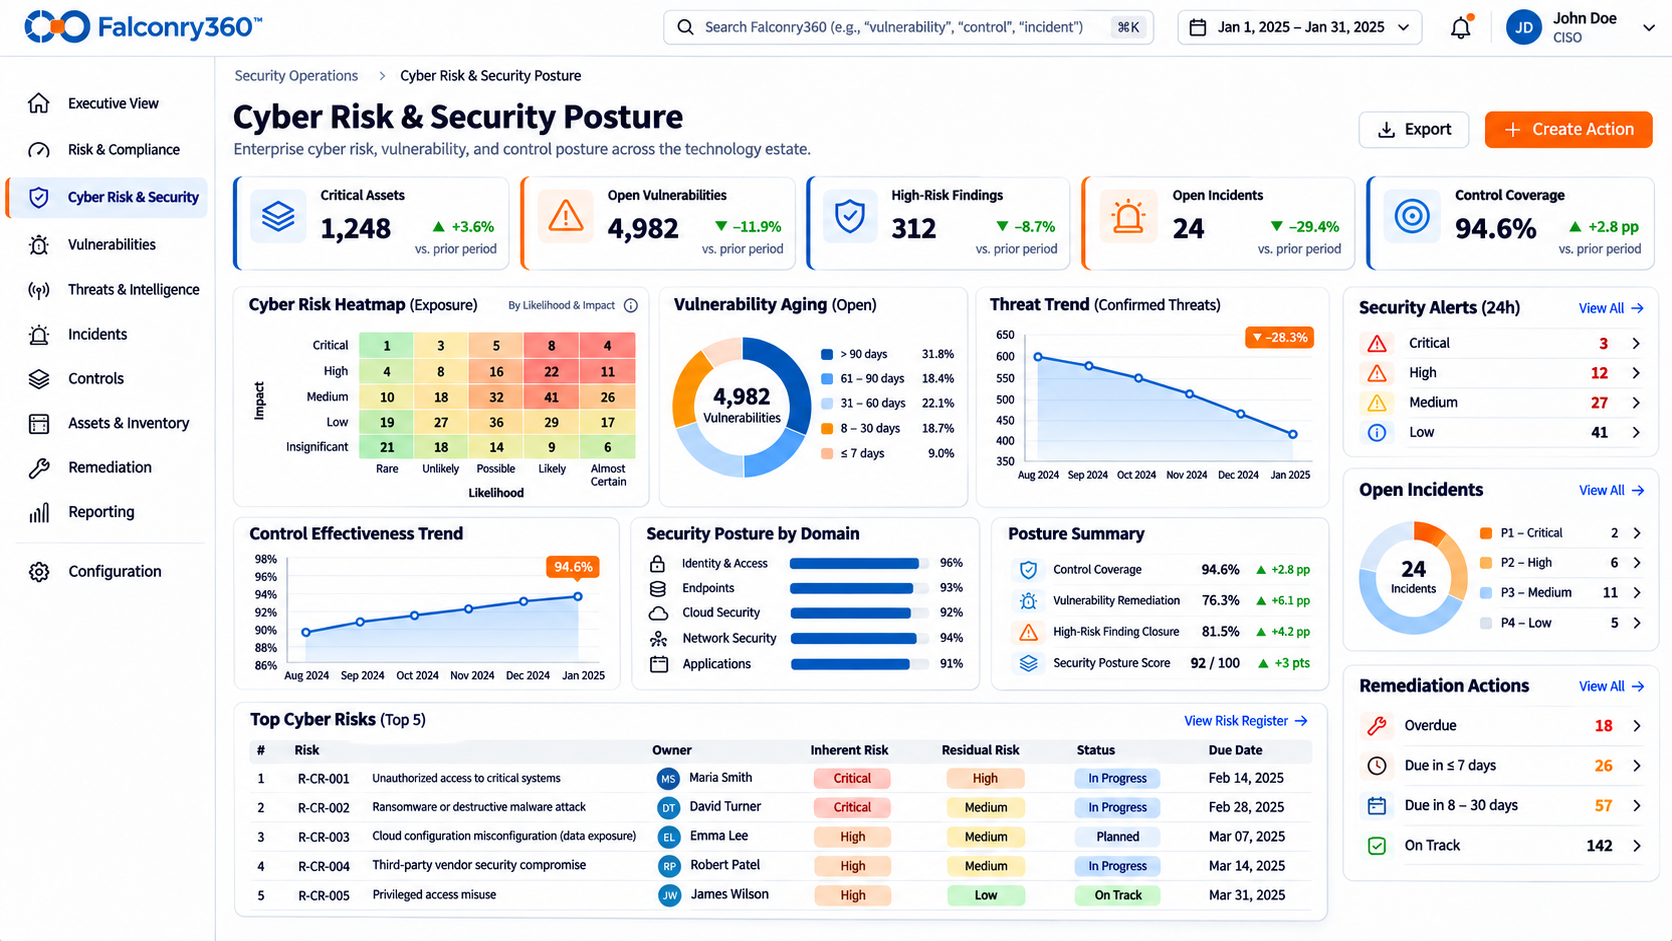
See exposure, control health and unresolved action together.
Give security and technology leadership a single operating view across cyber risk, control effectiveness, third parties and priority remediation.
- Cyber risk and control health
- Exceptions and remediation
- Executive trust posture
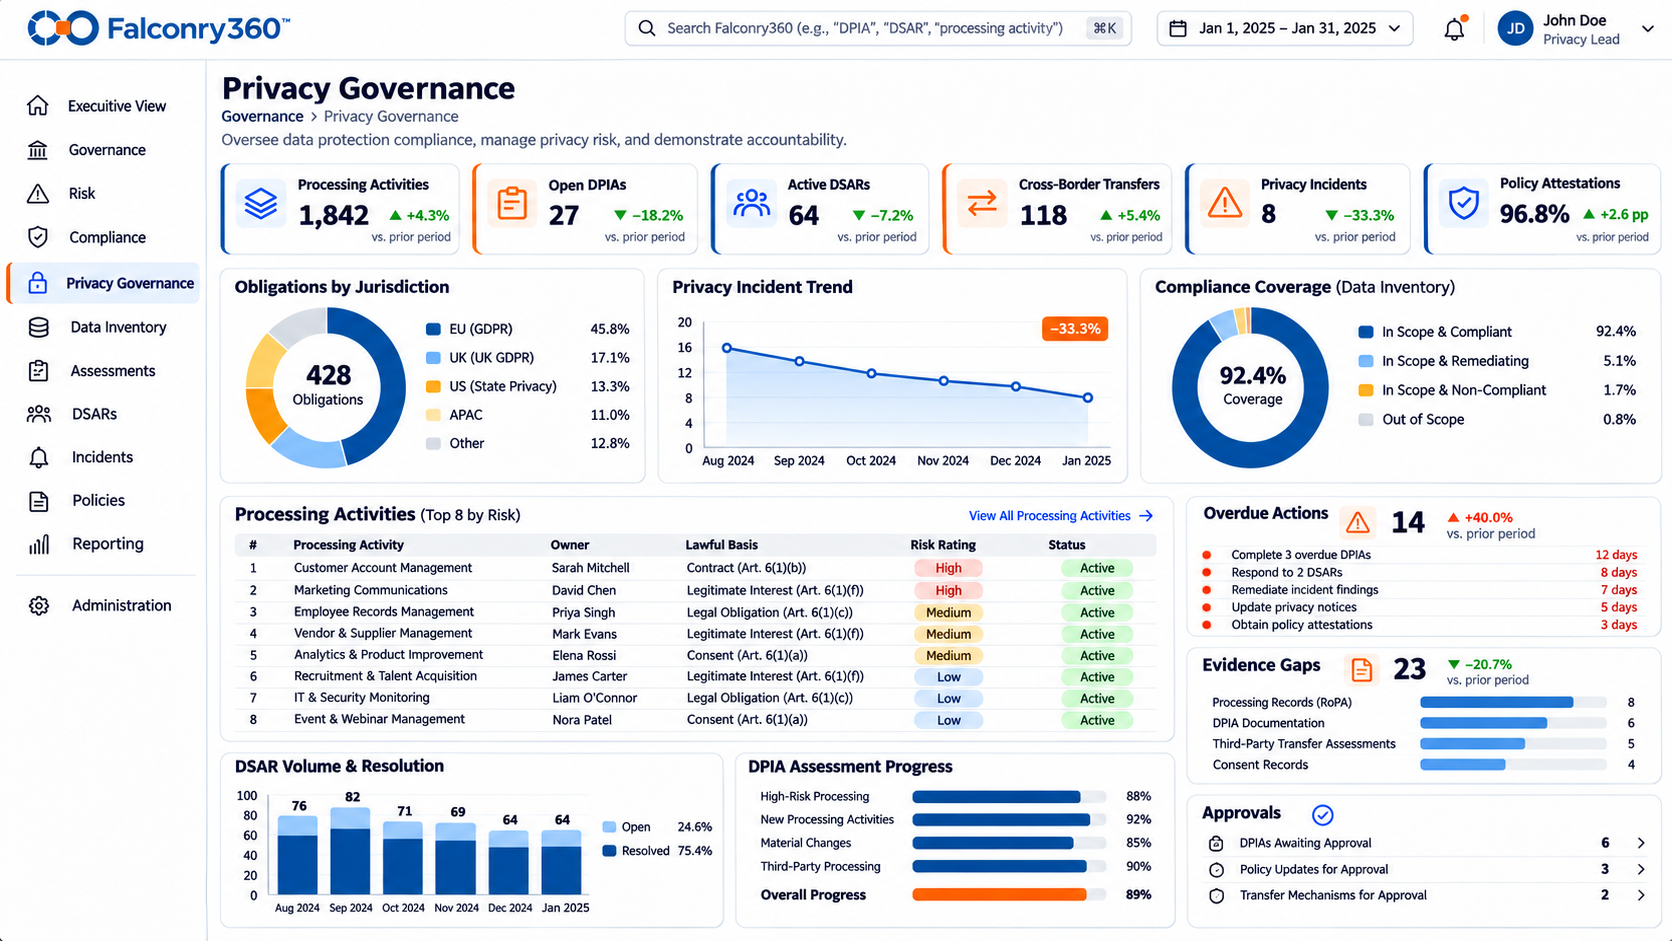
Move from privacy registers to governed accountability.
Connect processing, data, obligations, assessments, rights, controls and evidence instead of managing each privacy activity in isolation.
- ROPA and processing records
- DPIA / PIA workflows
- Rights, incidents and evidence
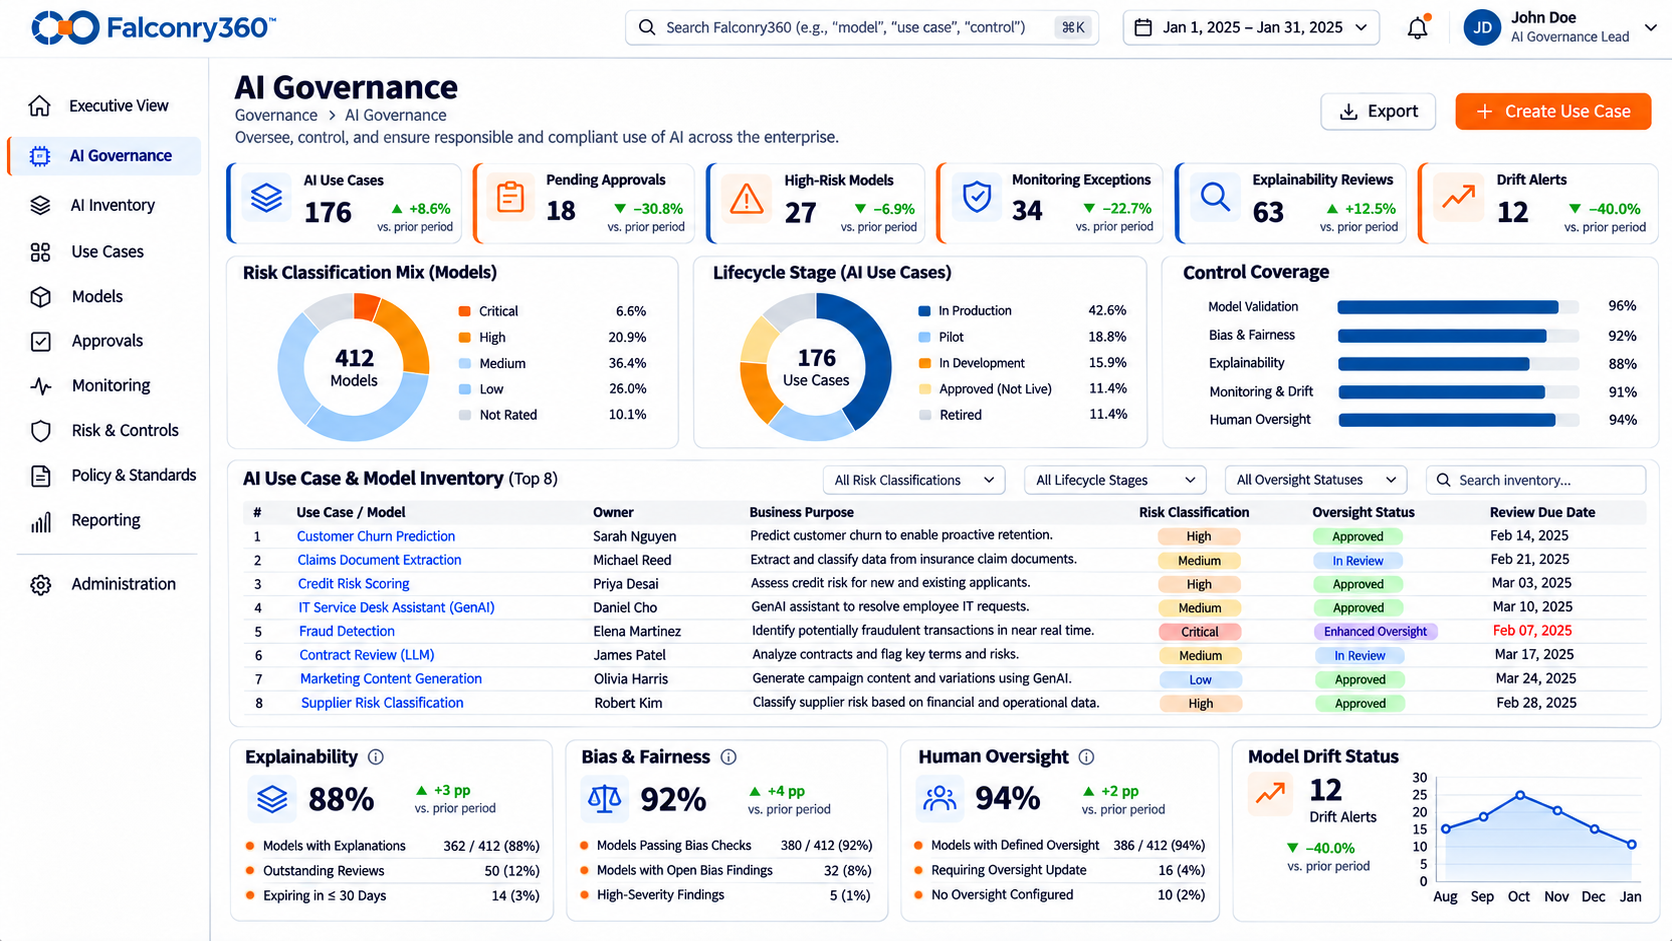
Know where AI is used, how it is classified and who is accountable.
Create a governed inventory of AI use cases with risk classification, approvals, obligations, controls and ongoing review.
- AI inventory and ownership
- Risk classification and approval
- Controls, evidence and monitoring
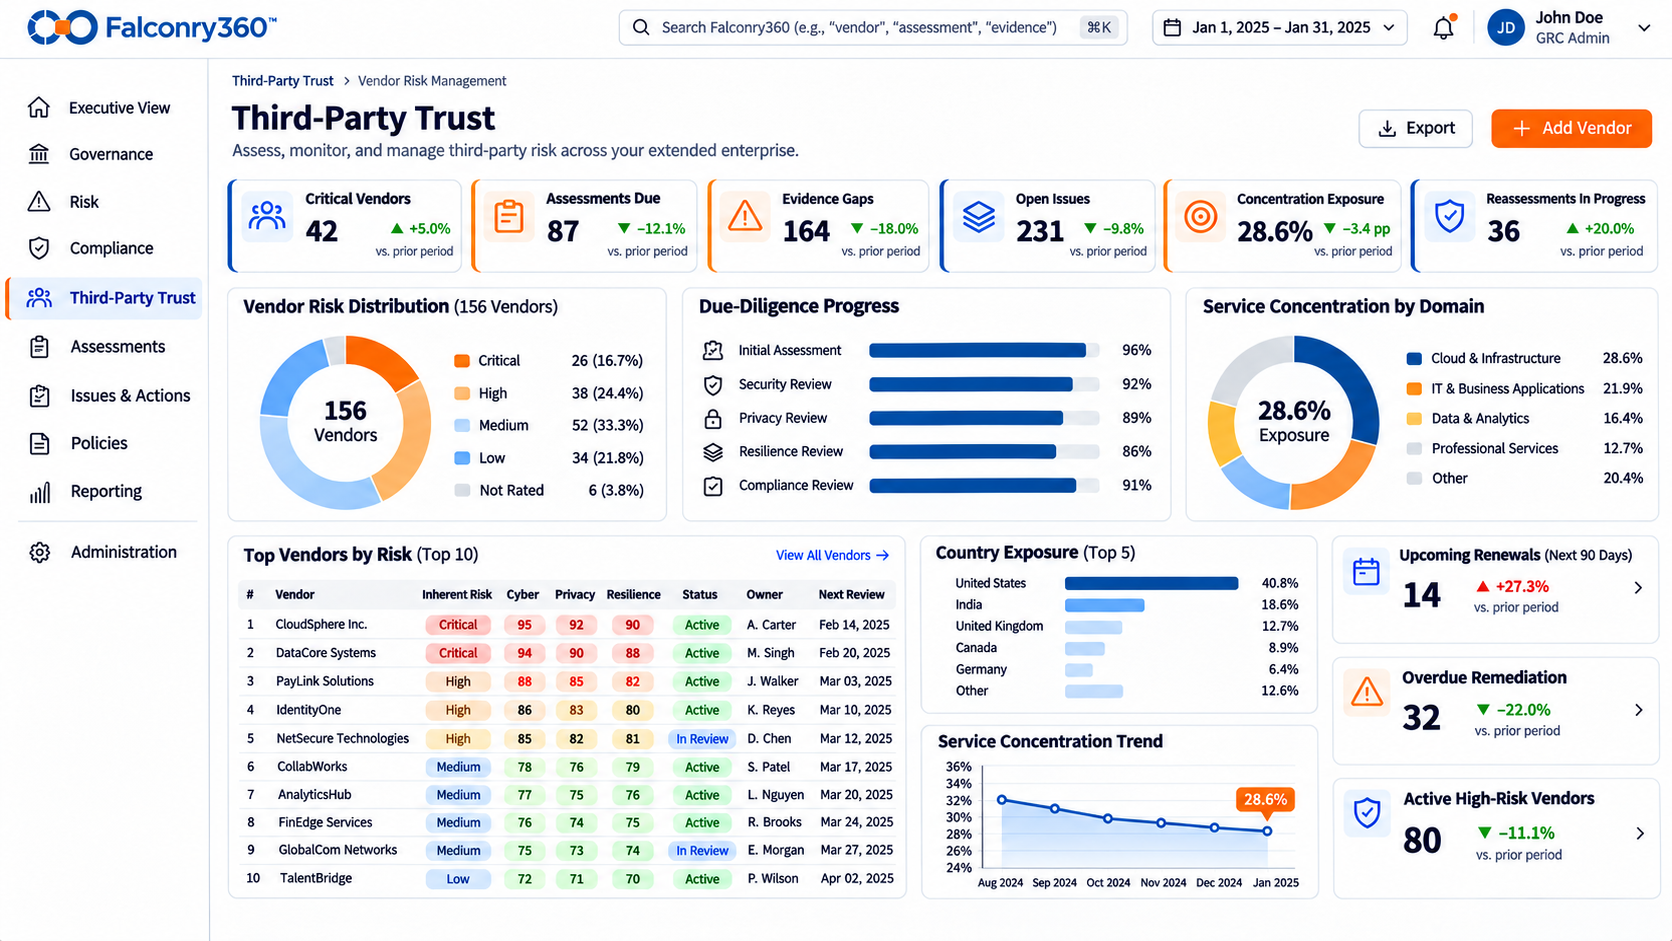
Assess vendors in the context of the services, systems and data they support.
Connect vendor criticality, assessments, evidence, issues and remediation to the business dependencies that make the risk material.
- Criticality and inherent risk
- Assessments and evidence
- Issues, remediation and review cycles
 FalconryX · Inside Falconry360
AI that interprets trust data without bypassing governance.
FalconryX works across governed cyber, privacy and AI records to help surface emerging exposure, interpret new rules, map controls, summarise evidence and prepare decision-ready trust narratives. Human review, source traceability and governance stay in the loop.
Trust decisions improve when security, privacy and AI governance can see the wider risk and assurance environment.
FalconryTrust shares governed records with adjacent propositions so risks, controls, issues, evidence and assurance do not need to be recreated.
Connect enterprise risk, obligations, controls and remediation to trust priorities.
Connected propositionFalconryAuditBring cyber, privacy and AI risks and evidence into risk-based assurance activity.
Connected propositionFalconryResilienceConnect security incidents and technology dependencies to resilience and recovery.
Connected propositionFalconryCultureLink policy, learning and attestations to control and conduct evidence.
Connected propositionFalconryAwareUse phishing, reporting and human-risk signals as part of cyber trust posture.
Regional depth. Global reach. One connected trust control environment.
FalconryTrust can structure obligations, mappings, evidence and reporting across cyber, privacy and AI governance requirements. The examples below are representative rather than exhaustive.
Representative trust priorities—not the limit of the proposition.
FalconryTrust supports a broad range of security, privacy and AI governance priorities. These areas illustrate common starting points rather than defining the limits of the operating model.
Cyber risk management
Connect threats, assets, vulnerabilities, controls, incidents and remediation to accountable risk ownership.
Privacy governance
Operate processing records, assessments, rights, controls and evidence through a governed privacy model.
AI governance
Inventory AI use, classify risk, assign owners, manage approvals and maintain evidence over time.
Third-party cyber & privacy risk
Assess vendors against the services, systems and data that make their risk material.
Control assurance
Reuse controls and evidence across requirements while tracking testing, exceptions and remediation.
Board & regulator reporting
Present exposure, compliance, control health and unresolved issues from the governed trust record.
See your cyber, privacy and AI governance environment on one trust record.
Explore FalconryTrust against your regulatory landscape, technology environment and governance priorities.