
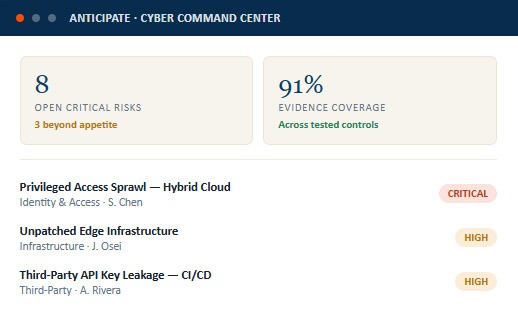
NCA, SAMA, ISO 27001, NIST CSF & more
ISO, NIST, SAMA, NCA, PDPL & more
Identity, Infra, Endpoint, Data, Cloud, Third-Party
Controls shared across 2+ frameworks
CVSS · EPSS · KEV-aware prioritisation
Requirements mapped to a control
Shared taxonomy, shared severity scale
Requirements without a control
Stop running cyber risk as a parallel program. Score it once, connect it to the enterprise register, and let one taxonomy carry it through to the board.
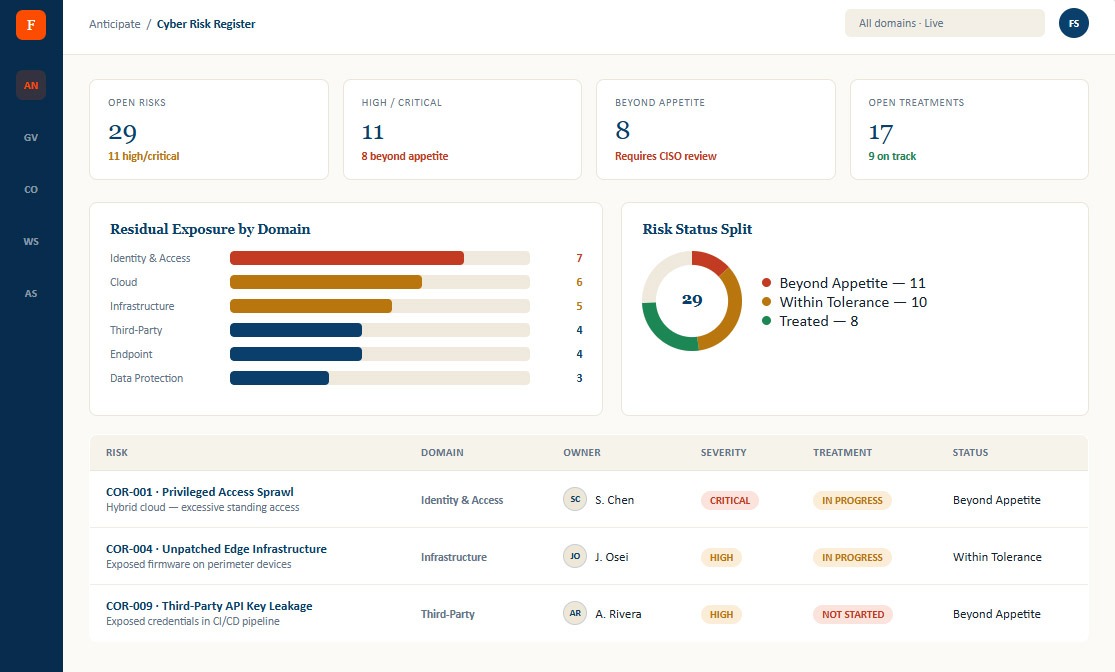
Every threat, vulnerability, and control gap scored against business impact and asset criticality — connected directly to the enterprise risk register, not siloed in a separate tool.
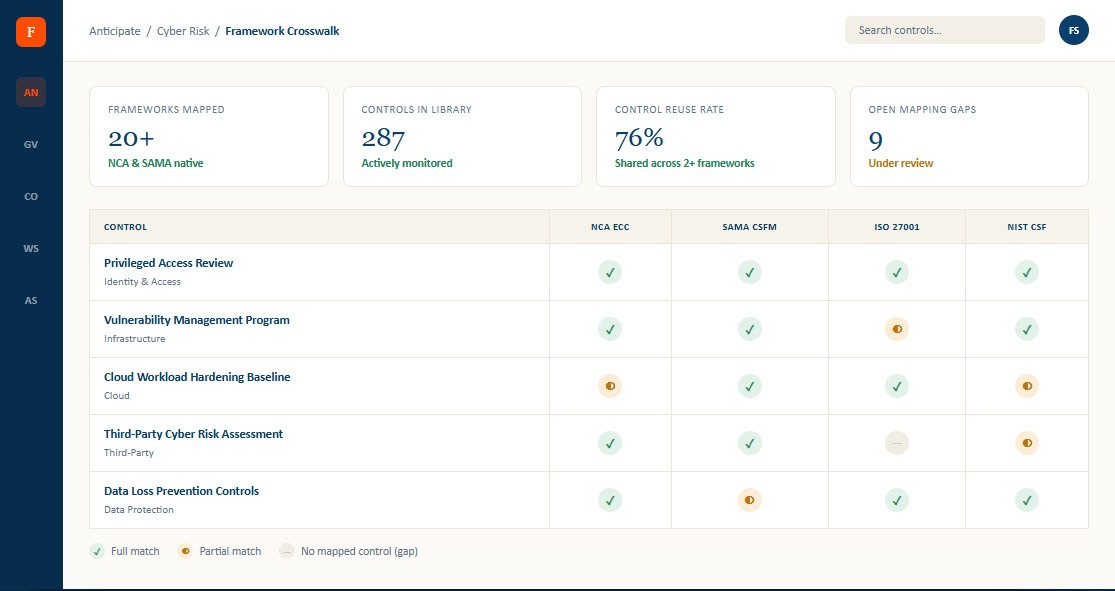
Map one control to NCA, SAMA, ISO 27001, and NIST CSF simultaneously — so a test or update reflects across every applicable framework automatically.
CVSS severity blended with EPSS exploit probability and CISA KEV status — so remediation capacity goes to what attackers are actually exploiting, not just what scores highest in isolation.
Six connected capabilities that turn scattered cyber data into a coherent, auditable risk posture — visible from the SOC to the board.
Cyber risk shares one taxonomy and one severity scale with the enterprise risk register — so CRO and CISO are reading the same number, not reconciling two.
Risk mapped across six operational domains — identity, infrastructure, endpoint, data, cloud, third-party — with risk-beyond-appetite flagged the moment a domain crosses tolerance.
Stop maintaining separate compliance spreadsheets for NCA, SAMA, and ISO 27001. One control, mapped to every applicable framework at once.
Real-time KRI dashboards and CVSS/EPSS/KEV-blended vulnerability scoring replace the quarterly snapshot — leadership sees actual posture, not a prepared presentation of it.
Every open risk becomes a treatment plan with an owner, a due date, and a visible before-and-after — so "in progress" actually means something.
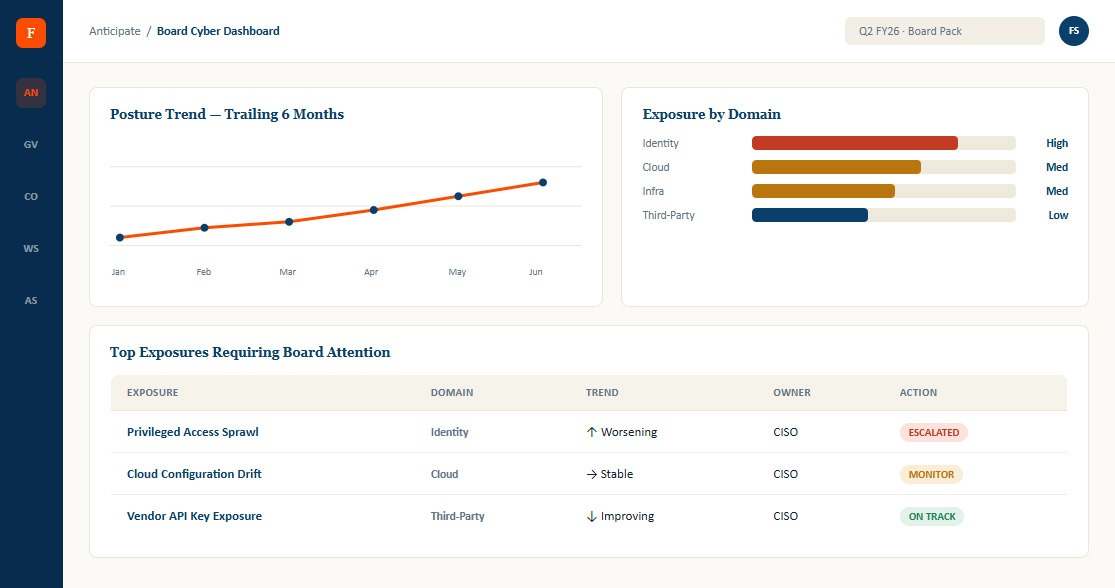
Exposure trend, domain concentration, and appetite status tracked automatically — board packs draft themselves with evidence already attached.
Three screens — the cyber risk register your team works in daily, the multi-framework crosswalk that keeps NCA and SAMA in sync, and the board dashboard that builds itself.
Every cyber risk scored against business impact and asset criticality, broken down by domain — with risks beyond appetite flagged automatically.
One control, mapped to every applicable cyber framework — so a single test or update reflects across NCA, SAMA, ISO 27001, and NIST CSF simultaneously.
Exposure trend, domain concentration, and appetite status — tracked automatically and ready before the board meeting, not the night before.
Capture every threat, vulnerability, and control gap, scored against business impact and asset criticality.
Link each risk to the control that mitigates it, mapped simultaneously to NCA, SAMA, ISO 27001, and NIST CSF.
CVSS, EPSS, and KEV status combine into one prioritised view — so remediation targets what's actually being exploited.
Every open risk becomes a treatment plan with an owner and a due date — tracked to closure, not just to assignment.
Exposure trend, domain concentration, and appetite status compiled automatically into the board cyber pack.
Cyber risk and enterprise risk share one register, one taxonomy, one severity scale
One control mapped to NCA, SAMA, ISO 27001, and NIST CSF at once — no duplicate spreadsheets
CVSS, EPSS, and KEV blended — remediation targets what attackers actually exploit
Every open risk is a tracked treatment plan — not an observation with no owner
FalconryX correlates threats to assets to controls to obligations — and tells you what to fix first
© 2026 Falconry360 . All rights reserved.