
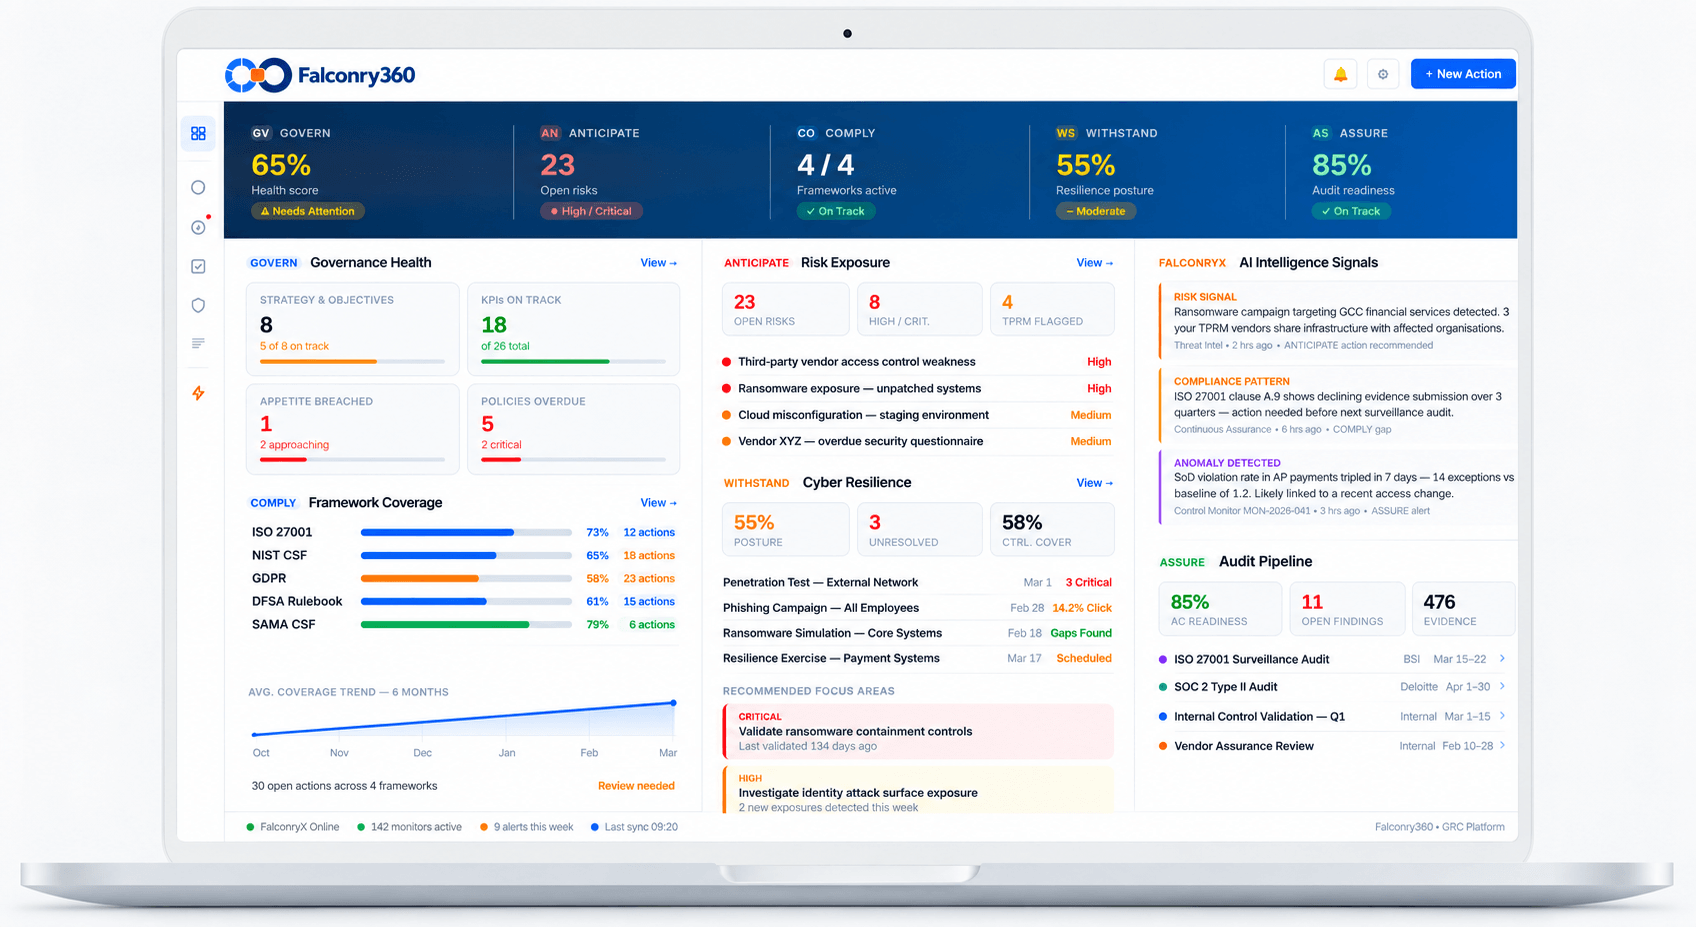
From board oversight to frontline control owners, Falconry360 gives every layer of the organisation the same real-time view of risk and compliance.
Regulatory expectations across the GCC are intensifying — SAMA, NCA, PDPL, and UAE NIAF are all evolving simultaneously. Traditional GRC tools weren't built for this velocity.
Risk registers live in spreadsheets. Audit findings sit in email threads. Compliance calendars are disconnected from business decisions. The result: blind spots at every level.
As organizations deploy AI, regulators demand accountability. Without structured AI governance, every deployment is a liability — and most organizations have no framework for it at all.
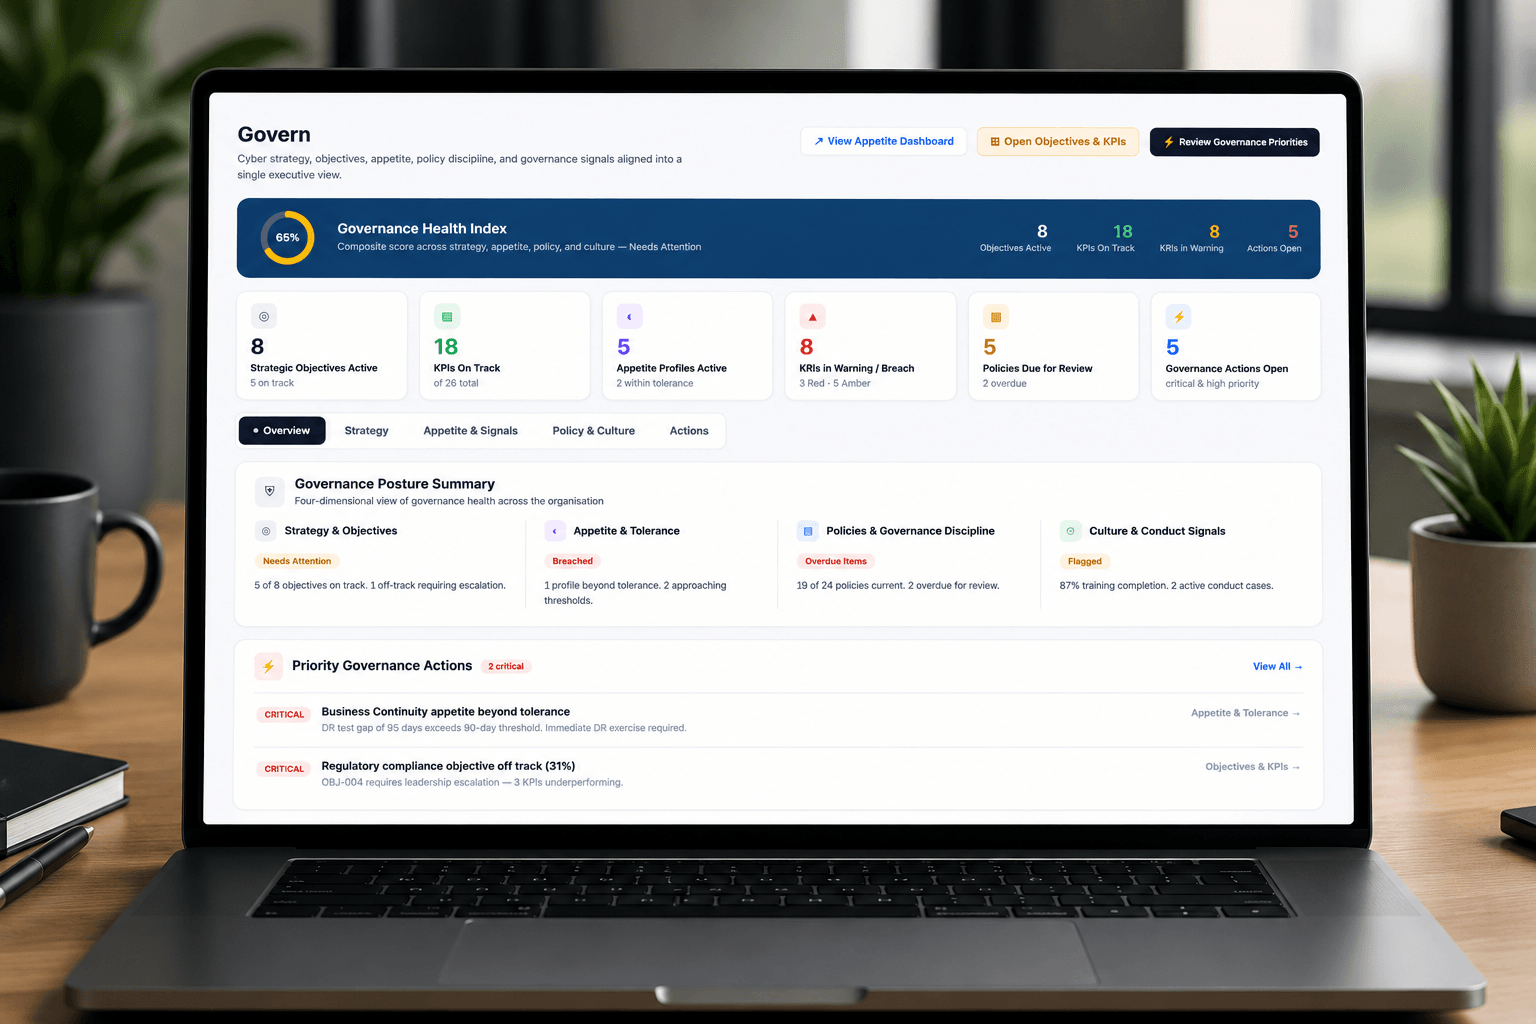
Align strategy, KPIs, objectives, and risk indicators.
Ethics, conflicts of interest, disclosures, and whistleblowing.
Policy lifecycle, approvals, attestations, and governance.
Awareness, training, certifications, and governance culture.
Responsible AI oversight, controls, and compliance.
Awareness, training, certifications, and governance culture.
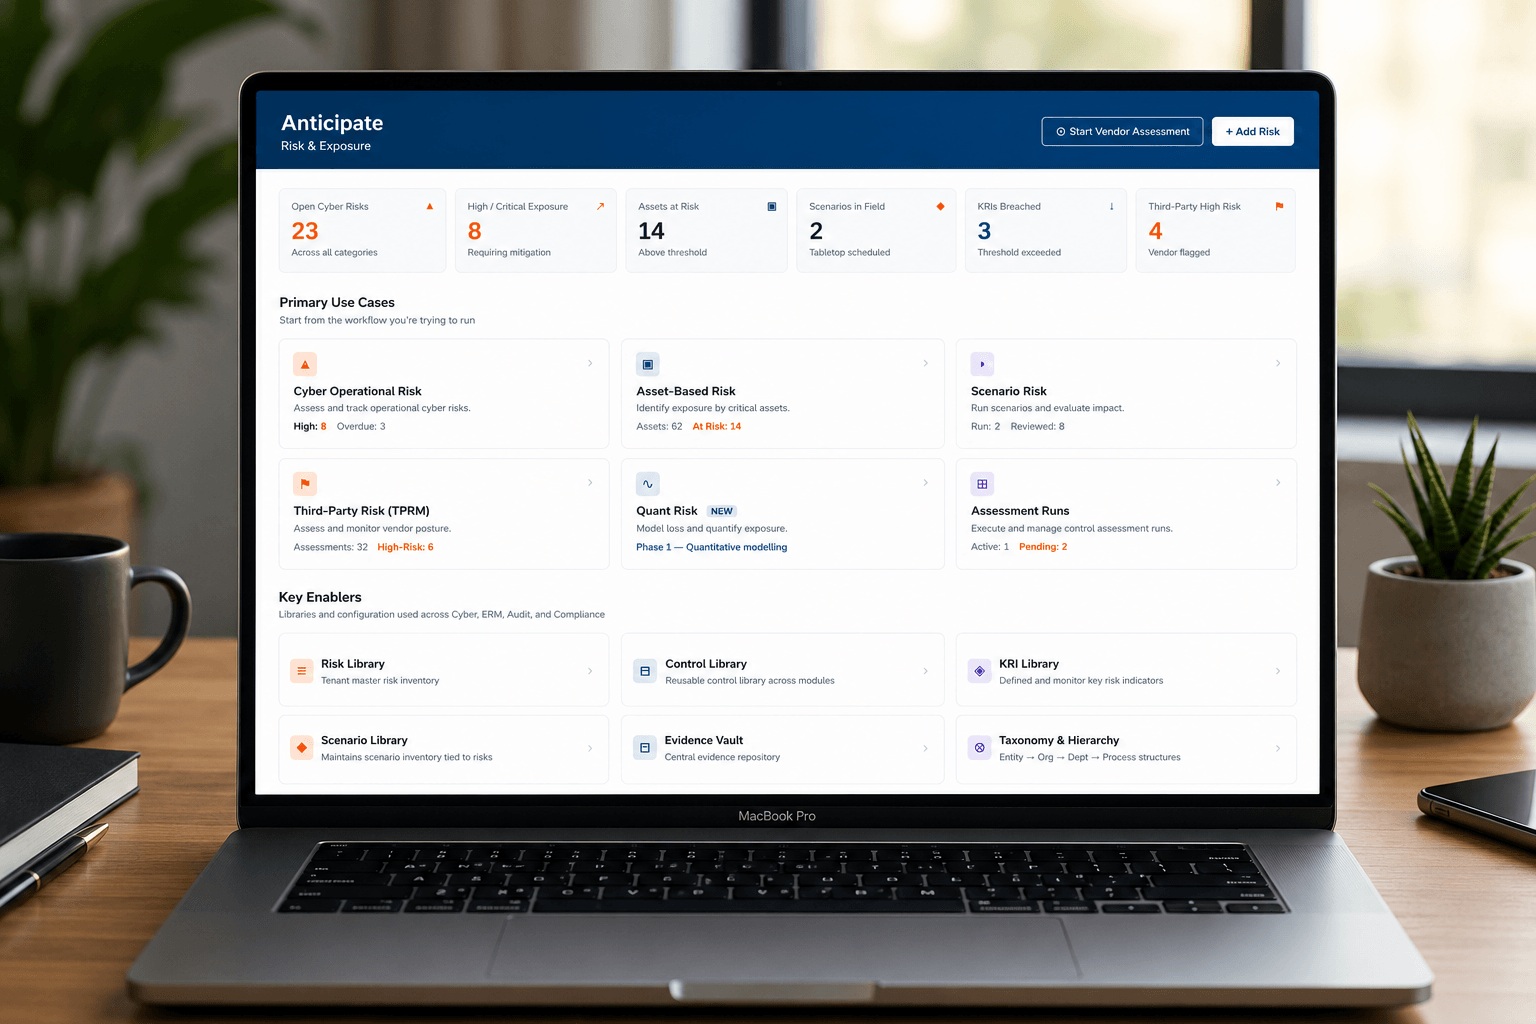
Enterprise-wide risk identification, assessment, and monitoring.
Vendor, supplier, outsourcing, and ecosystem risk.
Cyber posture, vulnerabilities, threats, and controls.
Process, people, systems, and operational loss events.
Privacy obligations, DPIAs, data governance, and PDPL.
Scenario analysis, financial impact, and risk modeling.
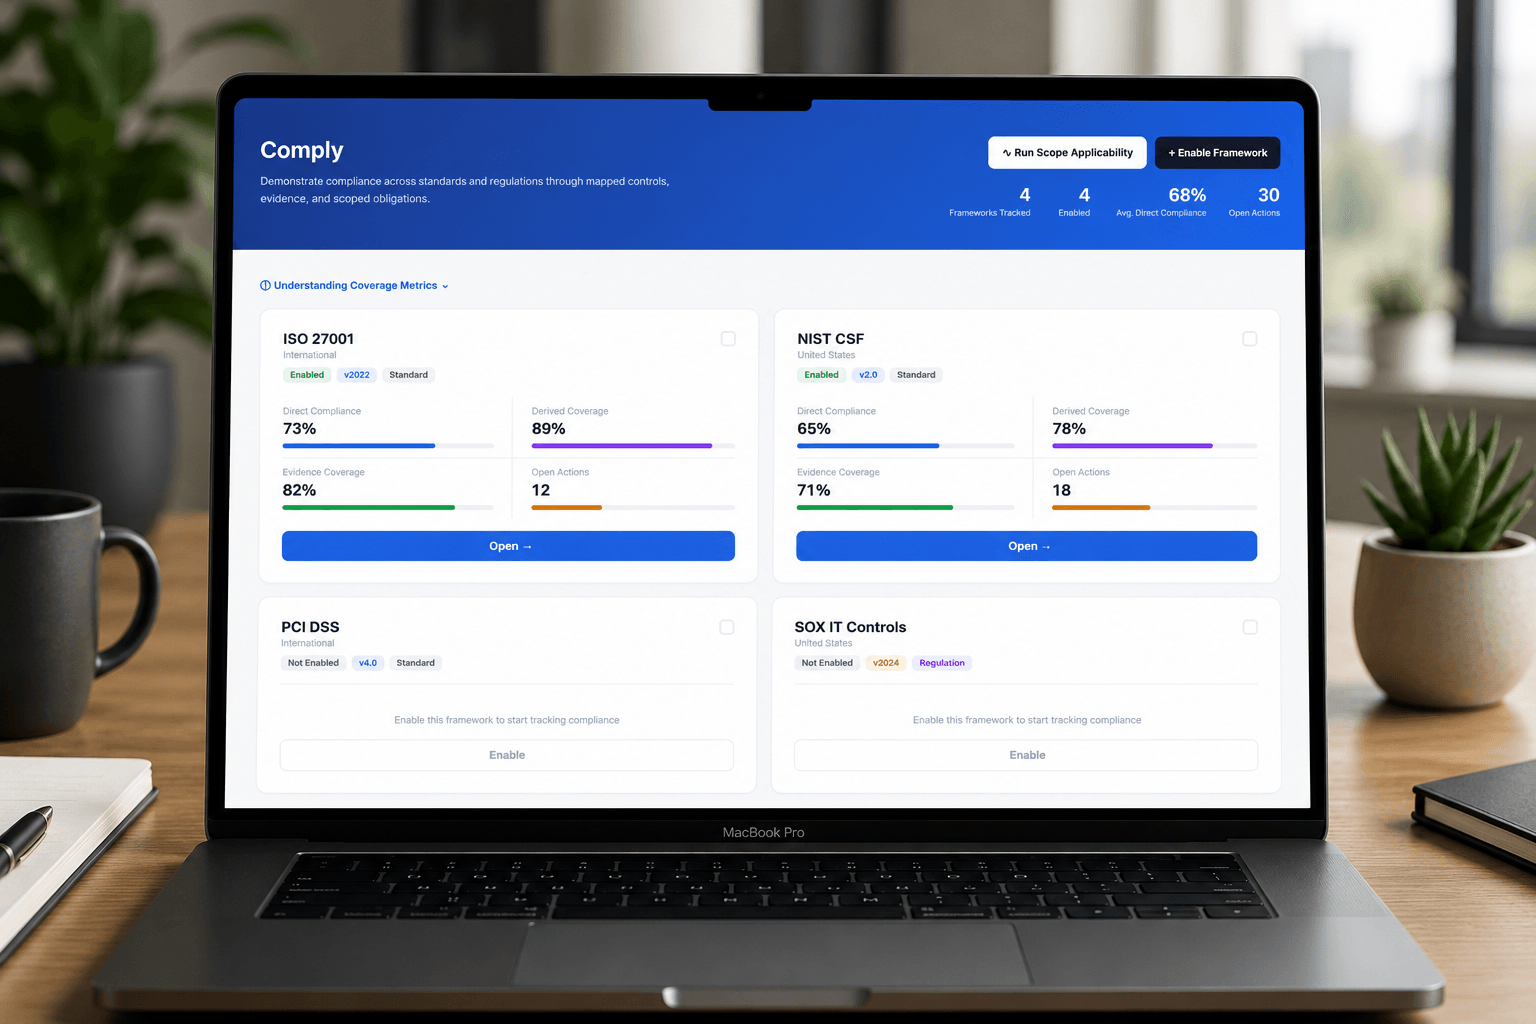
Centralized obligations, compliance responsibilities, and risk tracking.
Cybersecurity and outsourcing compliance oversight.
Map controls across regulations, standards, and frameworks.
Compliance incidents, investigations, and remediation.
Cybersecurity and outsourcing compliance oversight.
Strengthen resilience strategy and organizational preparedness.
Coordinate response, escalation, and crisis management activities.
Protect critical services through resilience planning and oversight.
Validate readiness through exercises, simulations, and stress testing.
Develop recovery strategies, continuity plans, and testing programs.
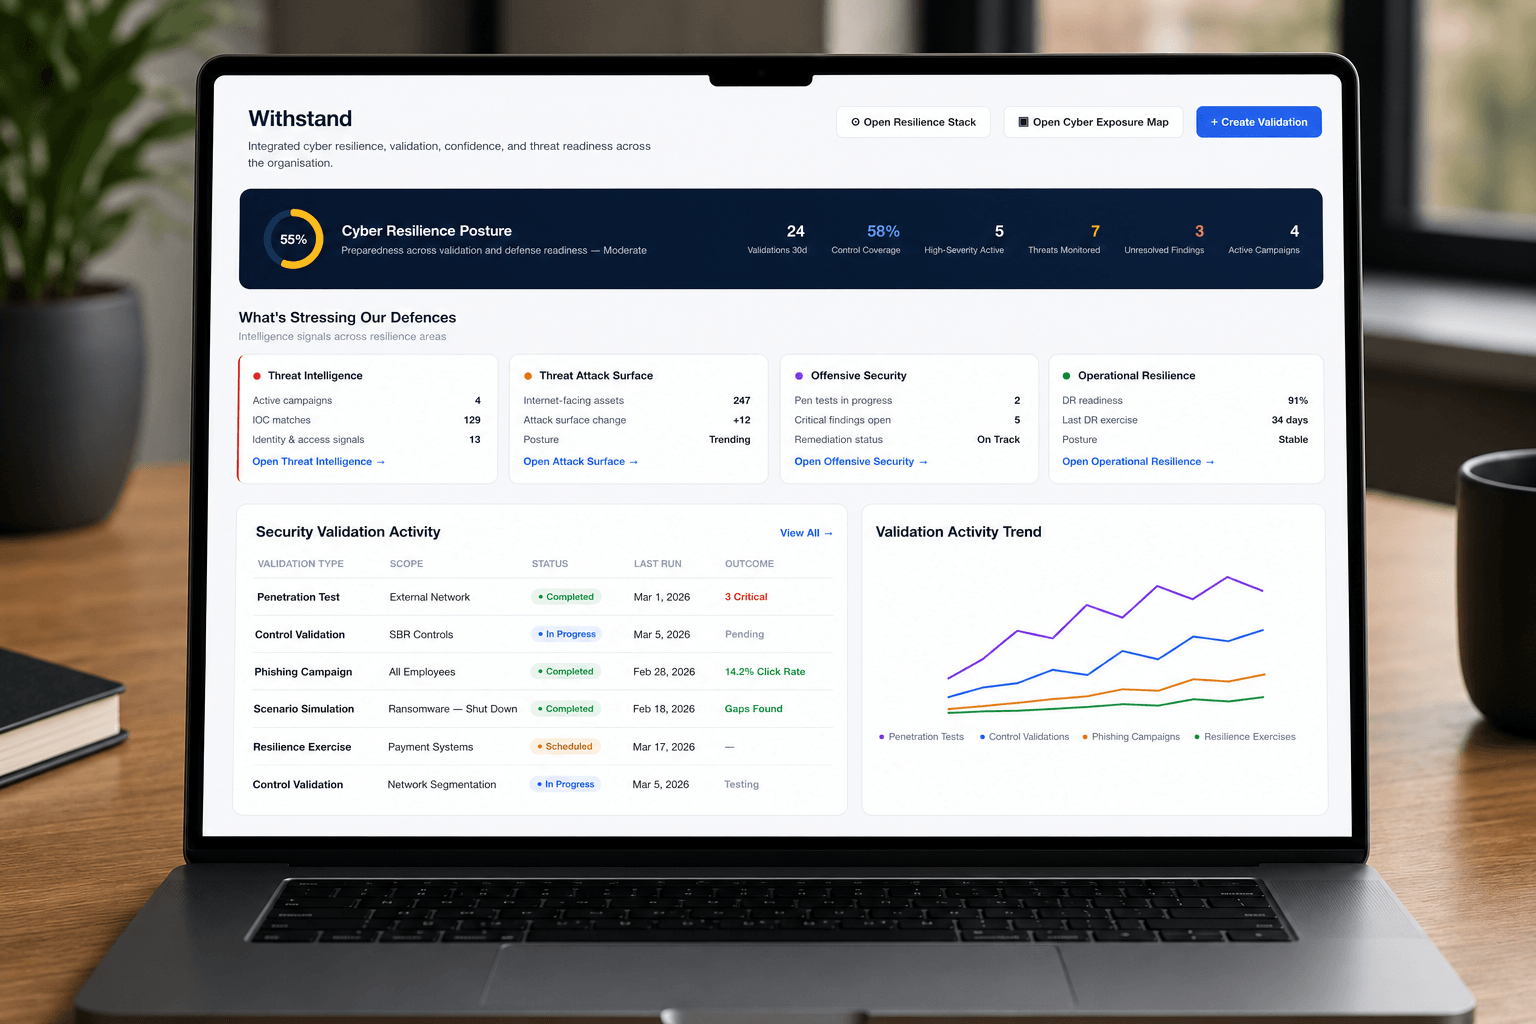
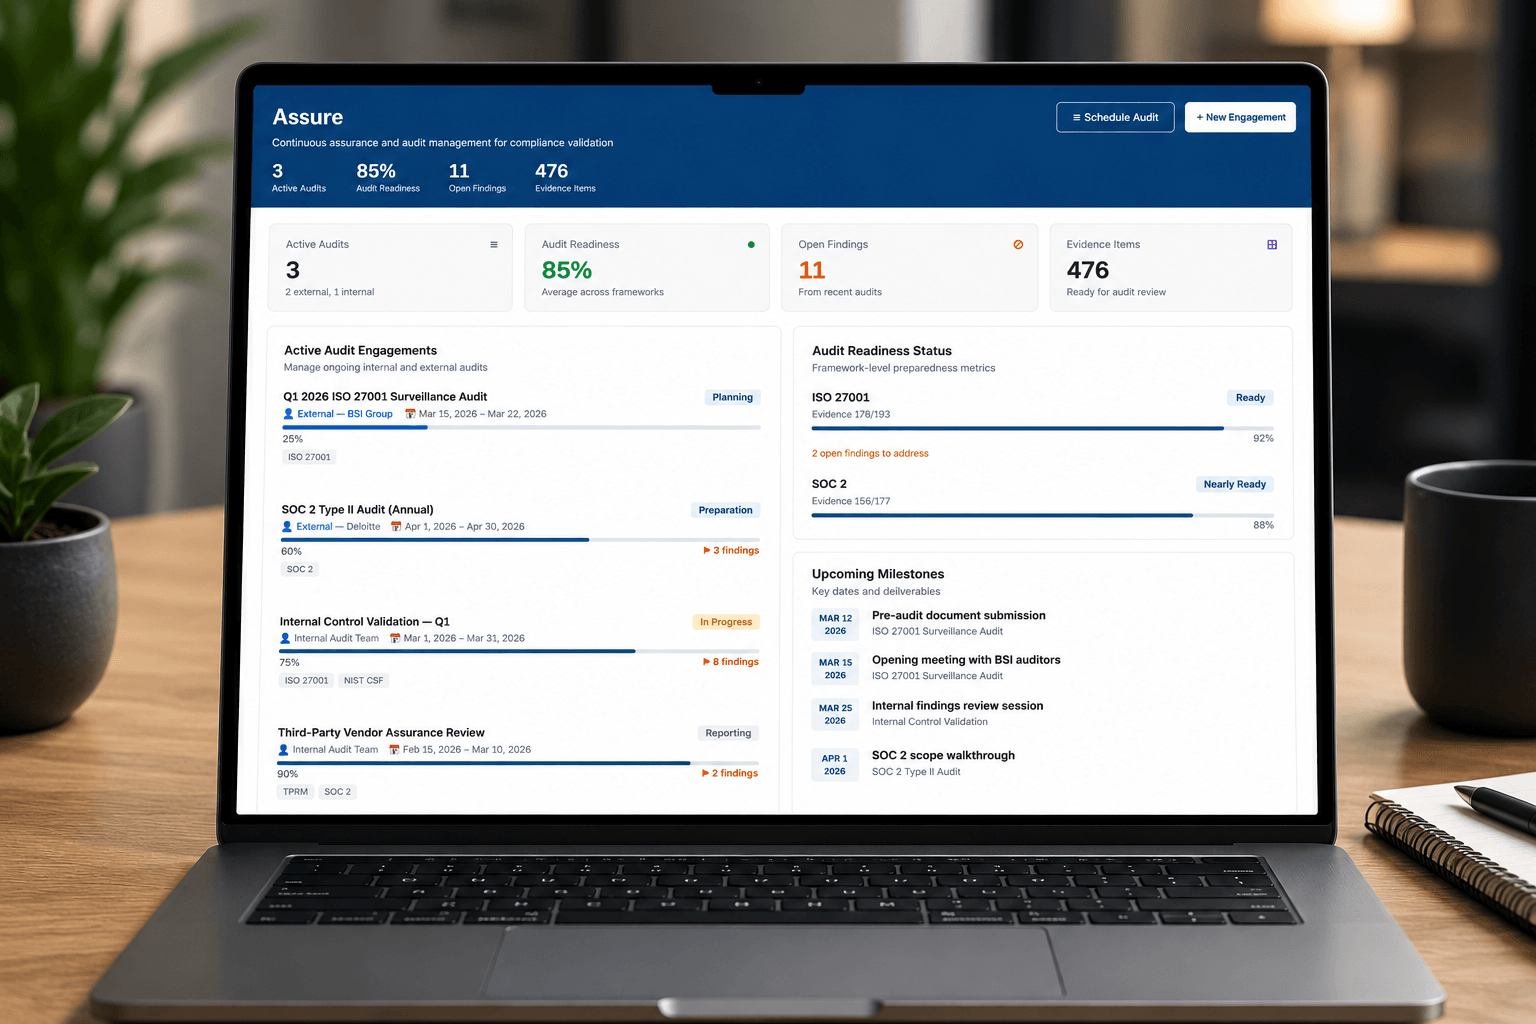
Plan, execute, and report risk-based audit activities.
Track findings, corrective actions, and remediation progress.
Test controls and strengthen financial reporting assurance.
Centralize evidence, audit trails, and assurance reporting.
Enable ongoing monitoring and automated assurance activities.
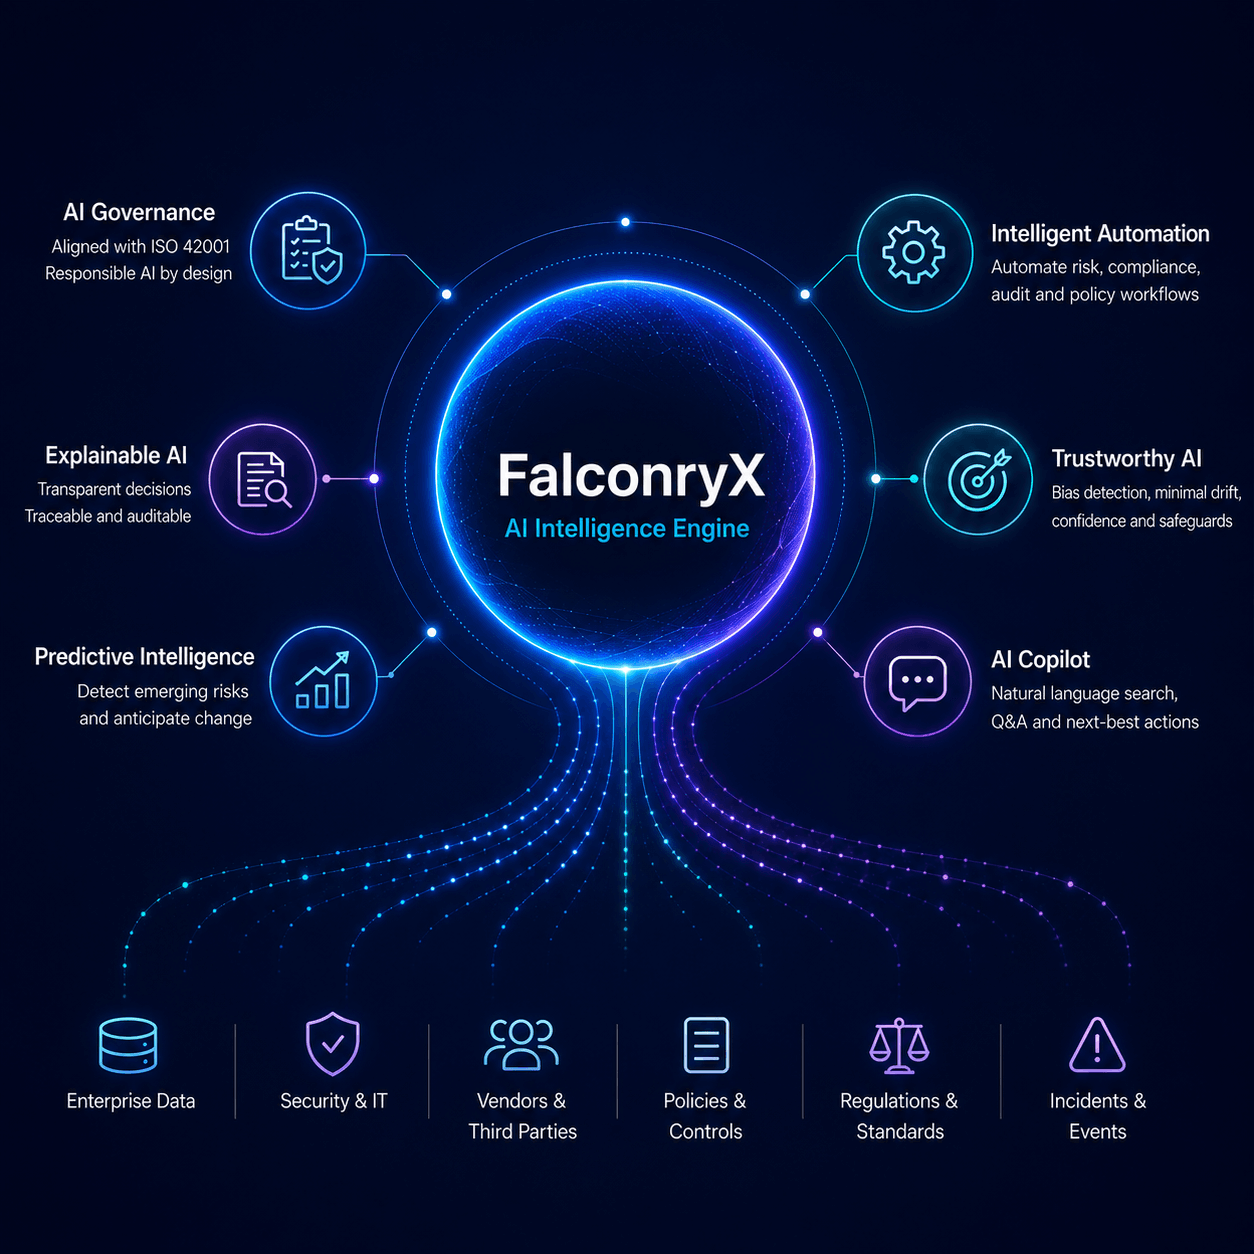
FalconryX is the AI layer powering every module of Falconry360 — turning your governance data into predictive signals, automated workflows, and explainable decisions your board can act on.
Risk summaries, control prioritization, and next-best-action suggestions — automatically surfaced for CROs, CISOs, auditors, and compliance teams.
FalconryX reads regulatory updates and automatically proposes obligation adjustments, framework crosswalks, and control gap assessments.
KRI drift detection, emerging risk pattern recognition, and early warning alerts — days before issues become incidents.
Every AI output is traceable. Human-in-the-loop review. Full audit trail. Built for organizations where explainability isn't optional.
Explore how Falconry360 brings regulatory compliance, enterprise risk, third-party risk, cyber and technology risk,
resilience, and assurance into one connected operating environment.
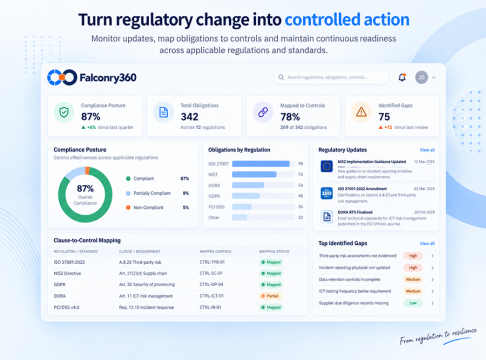
Track regulatory updates, map obligations to controls, identify gaps and maintain continuous readiness across applicable regulations and standards.
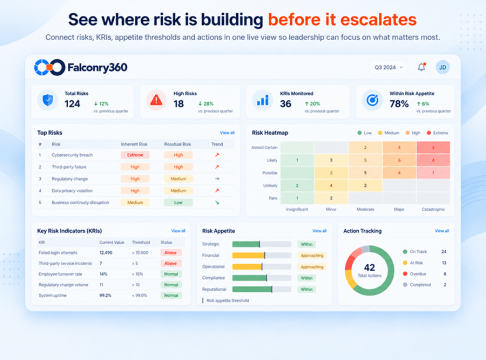
Connect risks, KRIs, appetite thresholds and actions in one live view so leadership can focus on where exposure is changing and what needs attention.
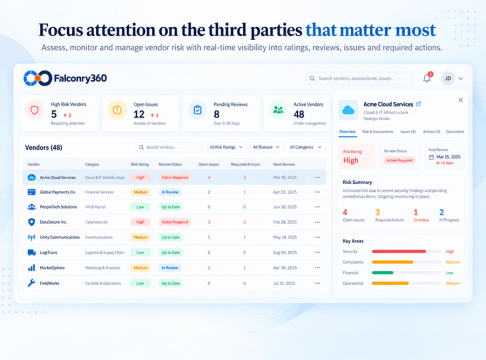
Assess, monitor and manage third-party risk with clear visibility into ratings, reviews, issues, dependencies and required actions.
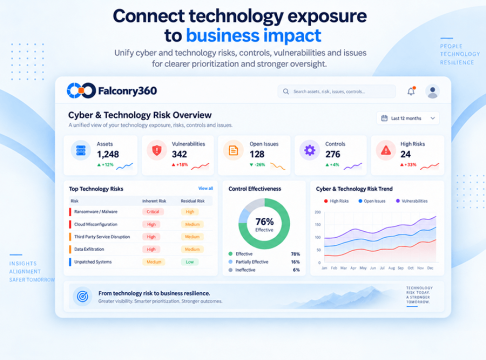
Bring cyber and technology risks, controls, vulnerabilities and issues into one view for stronger prioritisation, oversight and decision-making.
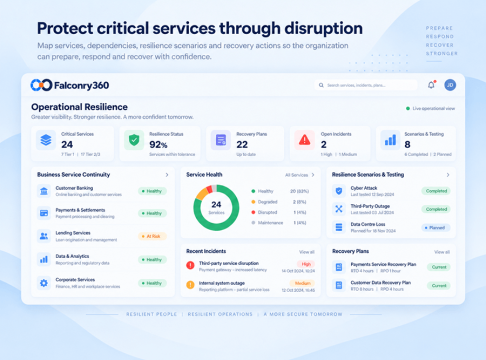
Map critical services, dependencies, scenarios and recovery actions so teams can prepare, respond and recover with confidence.
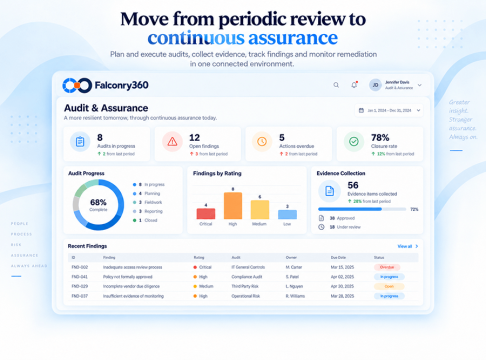
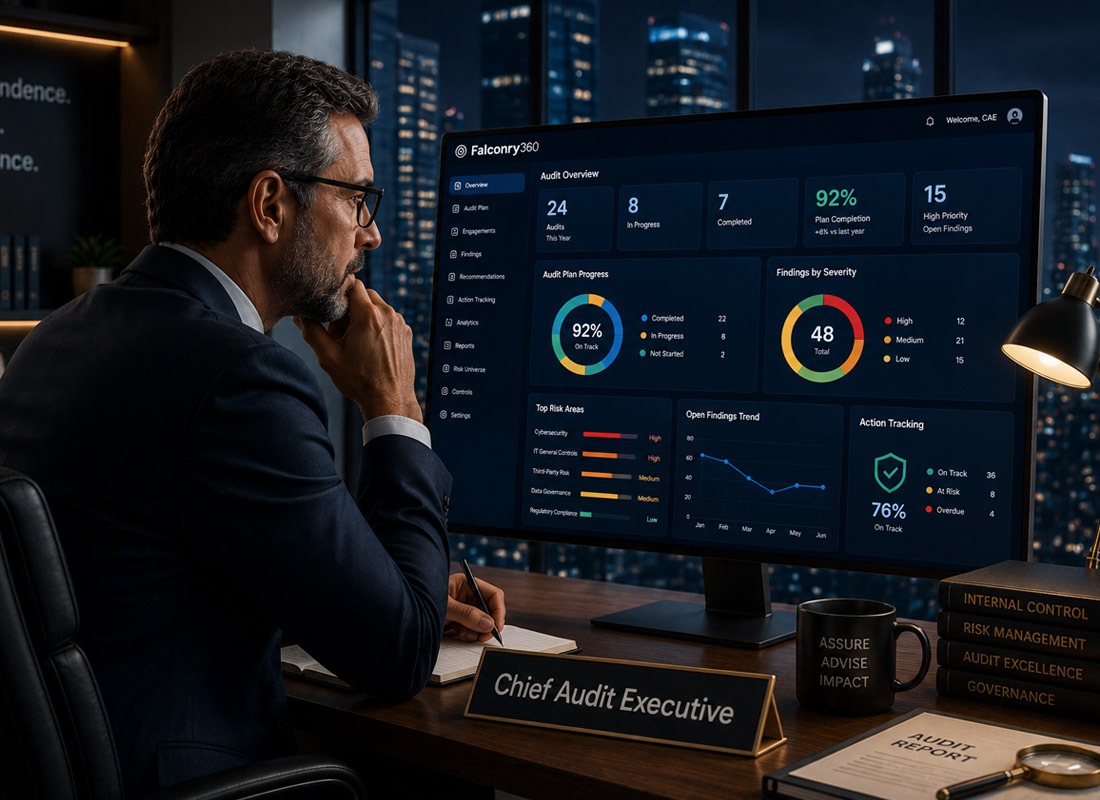
Plan and execute audits, collect evidence, track findings and monitor remediation in one connected, traceable environment.
Falconry360 ships pre-configured for the regulations your business must comply with GCC-native and globally recognized.
Stop building from scratch.

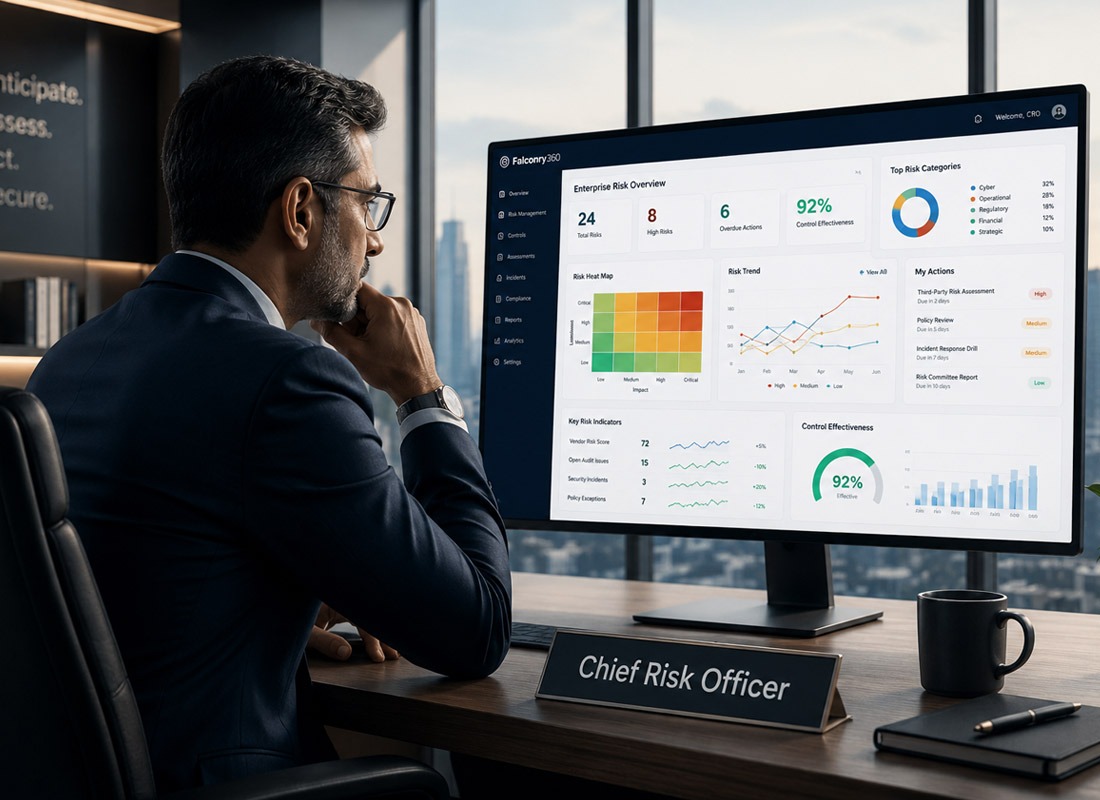
Stop chasing risk data across five different systems. Falconry360 gives CROs a single, real-time risk intelligence engine — from strategic KRIs to operational exposures — with board-ready reporting built in.
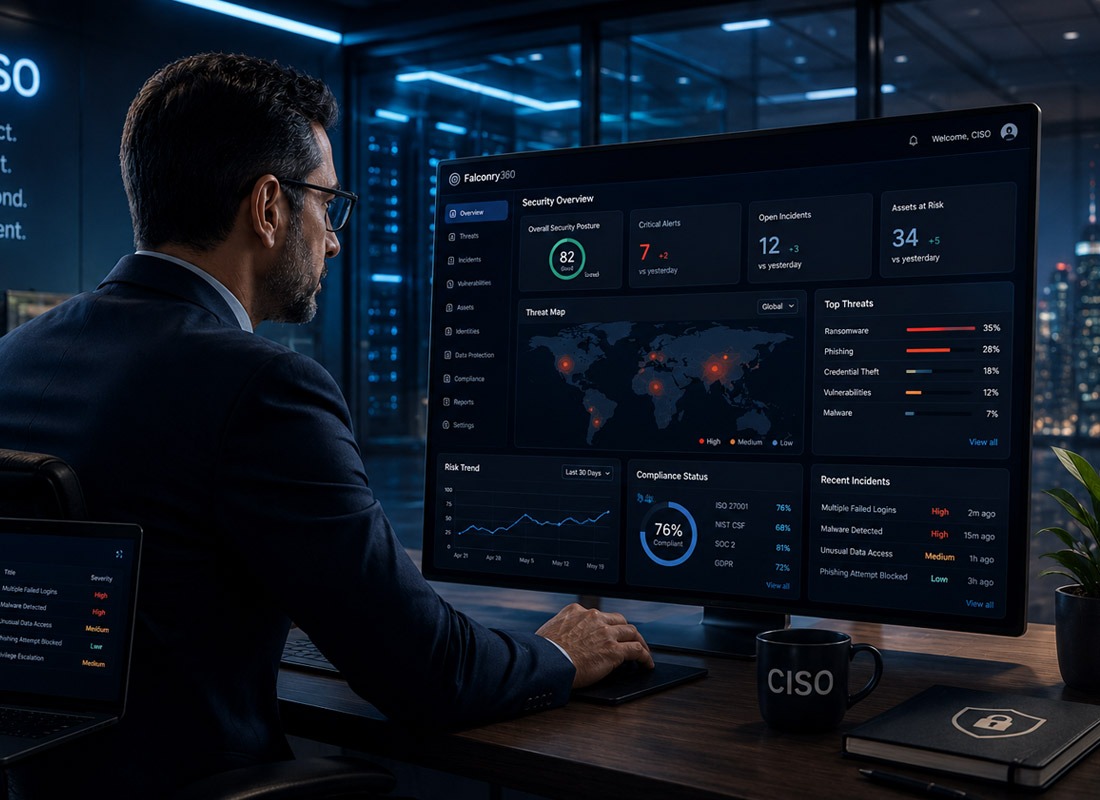
Align your security controls to NCA ECC, NIST CSF, and ISO 27001 simultaneously. Track gaps, evidence compliance, and report to the board in the language they understand.
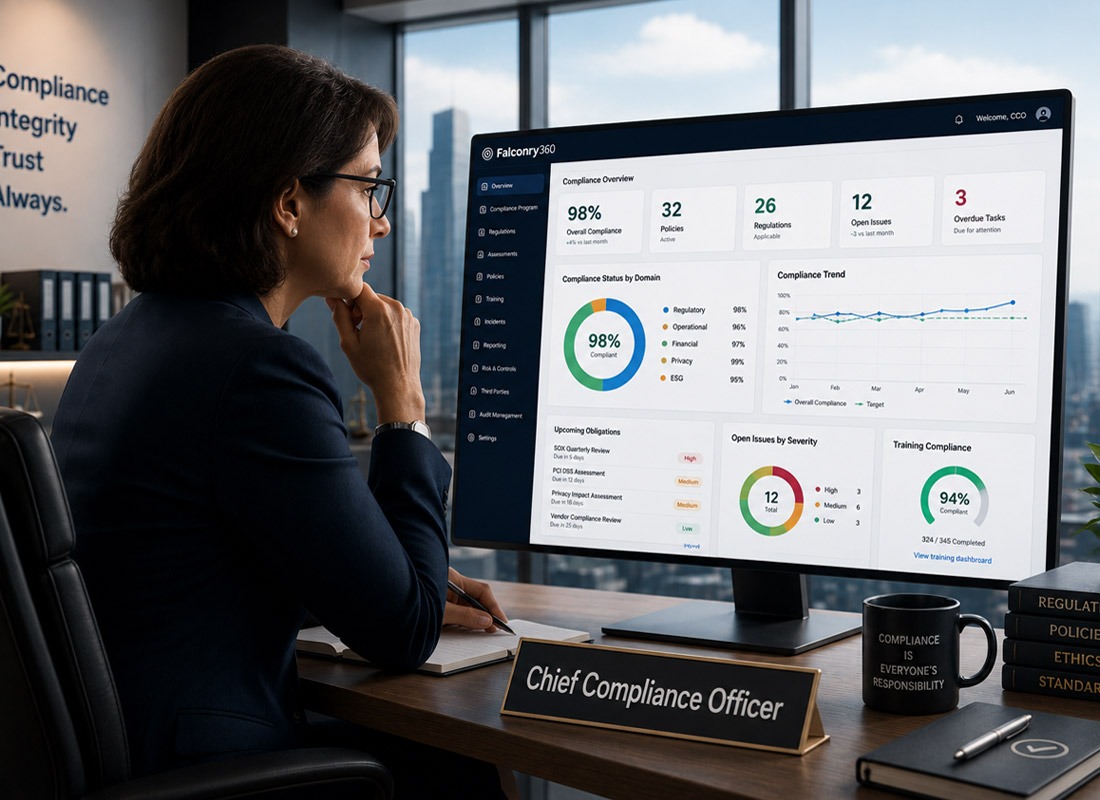
Track every obligation across every jurisdiction your business operates in. When regulations change, Falconry360 tells you what changed, what it affects, and what to do next automatically.
Move from annual audit plans to continuous assurance. Falconry360 connects your audit universe to the live risk register, so your teams always work where risk is highest.
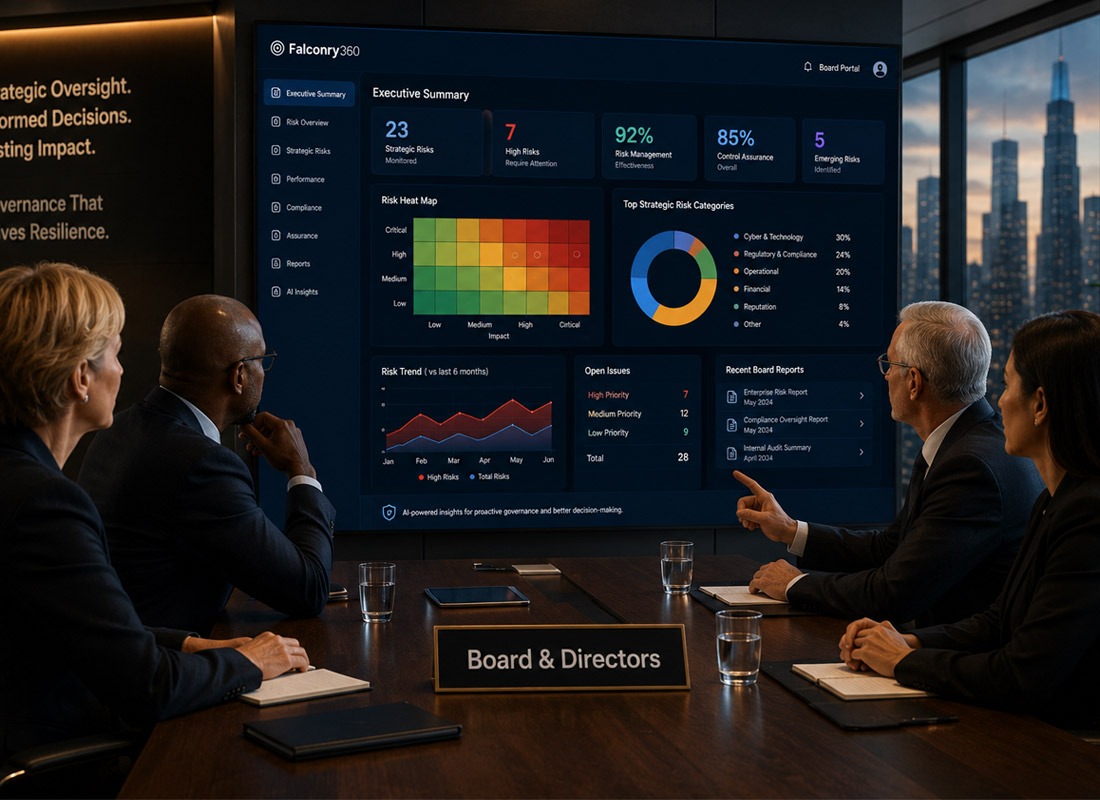
Boards shouldn't need 80-page risk reports. Falconry360 delivers a single-screen view of organizational risk, compliance status, and governance health designed for executive clarity, not analyst depth.


See Falconry360 in a focused 30-minute executive walkthrough
tailored to your industry and your regulatory environment.
© 2026 Falconry360 . All rights reserved.