
Across all assurance activities
Items referenced in 2+ activities
Board, audit committee & regulatory
Tamper-proof, timestamped log
Internal audit workpapers, ICFR test results, continuous monitoring records, and regulatory submissions — stored once, referenced everywhere, with a tamper-proof chain of custody.
Every piece of evidence from every assurance source — audit workpapers, test results, policy confirmations, and regulatory submissions — stored in one structured, searchable repository.
Every action in the platform — evidence upload, reviewer sign-off, issue creation, report approval — is logged automatically with a timestamp, user, and tamper-proof chain of custody.
Board packs, audit committee papers, and regulatory submissions generated directly from live engagement data — not manually assembled from emails, shared drives, and spreadsheet exports.
Falconry360 ensures every assurance conclusion is backed by retrievable evidence, every action is logged, and every report is reproducible — so no auditor ever has to assemble a paper pack from scratch.
Upload, classify, and tag evidence items against controls, engagements, frameworks, and obligations. Every item is versioned and linked to the assurance activity that produced it — retrievable in seconds.
Reference a single evidence item across multiple assurance activities — internal audit, ICFR testing, regulatory submission — without duplicating files or creating version drift.
Every platform action is logged automatically — user, timestamp, before and after state — producing an immutable chain of custody that satisfies external auditor, regulator, and forensic review standards.
Auto-populate board packs, audit committee papers, and CAE reports directly from engagement data — including issue summaries, plan status, and completion metrics — without manual compilation.
Bundle evidence, workpapers, and test results into a structured reliance package for external auditors or a regulatory submission package — structured, complete, and ready for handover.
Define retention schedules by evidence type and jurisdiction — with automatic archiving at the end of the retention period and a permanent index of what was held, when, and why it was disposed.
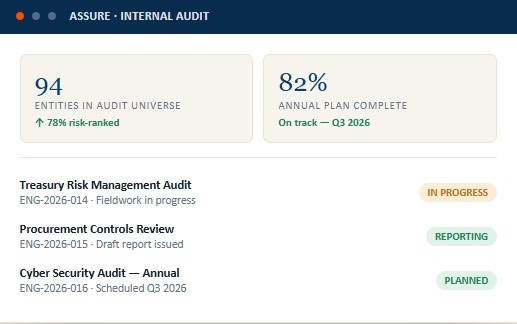
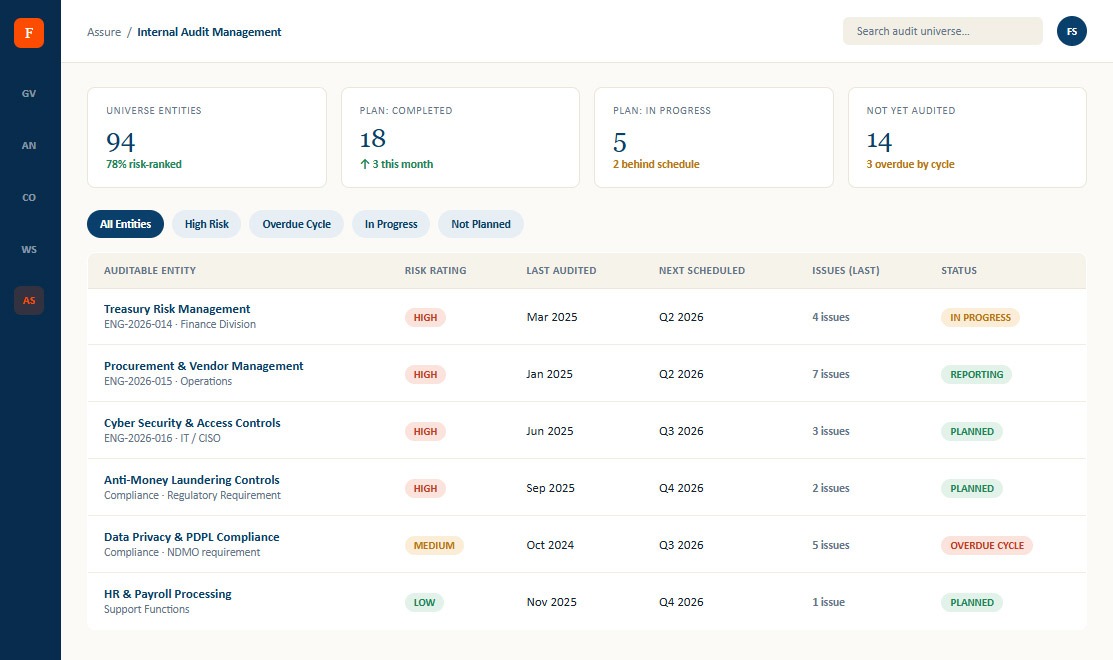
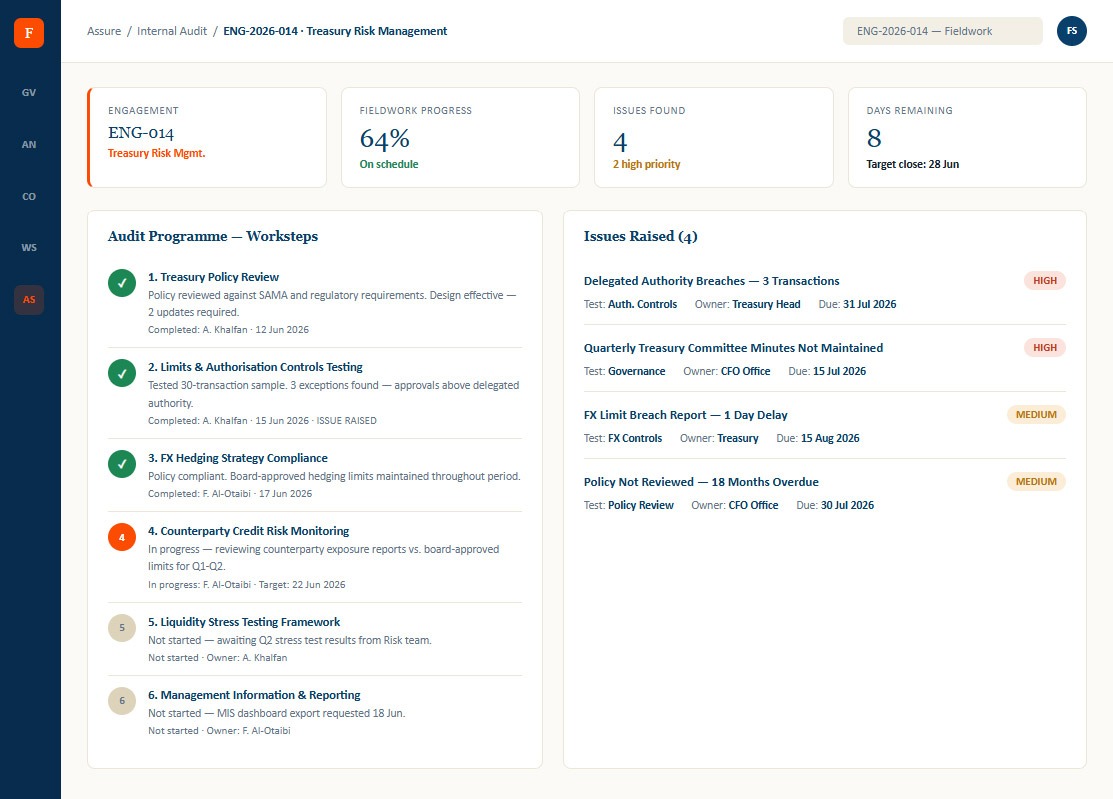
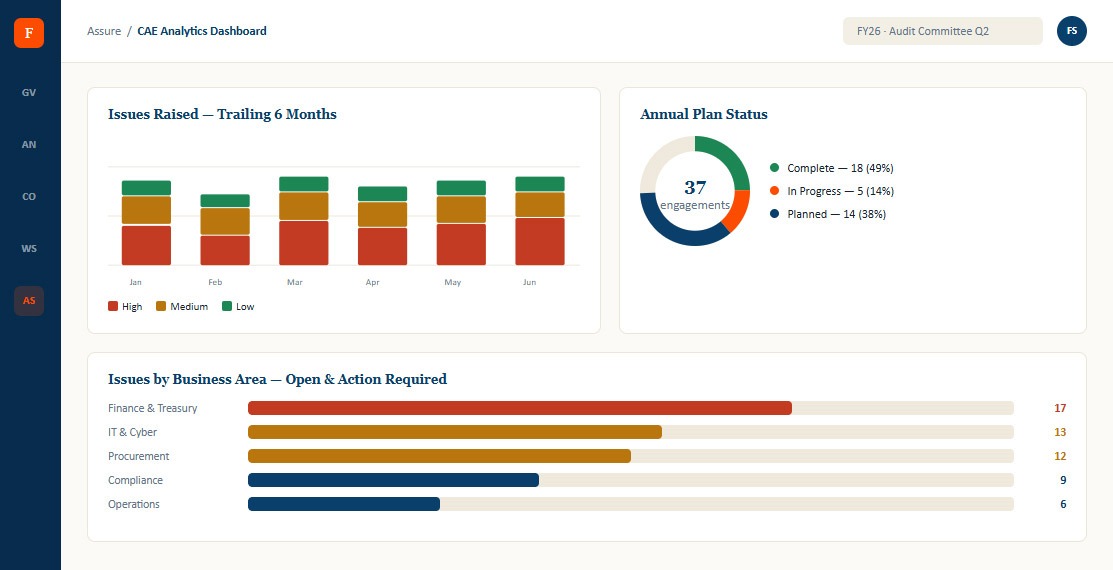
Three screens — the centralised evidence vault your assurance team maintains, the audit trail log that regulators and external auditors rely on, and the assurance report pack your board receives.
Every evidence item from every assurance activity — searchable, tagged, version-controlled, and linked to the control, engagement, or obligation it supports.
An immutable, timestamped record of every platform action — who did what, when, and to which record — satisfying external auditor, regulator, and forensic review requirements.
An auto-generated assurance report — plan status, issue summary, key findings, and CAE opinion — produced directly from live engagement data without manual compilation.
Evidence is captured during the assurance activity — audit workpapers, test results, or monitor outputs — and tagged automatically to the relevant control, engagement, and obligation.
Evidence items route to the designated reviewer — senior auditor, controller, or compliance officer — for quality review and sign-off, with every step logged in the audit trail.
Evidence is linked across activities — audit workpapers reused in ICFR packages, monitoring results referenced in regulatory submissions — without duplicating files or creating version drift.
Board packs, audit committee papers, and regulatory submissions are populated from live engagement data — the report structure is fixed, but the content is always current.
Evidence is retained according to the defined schedule and jurisdiction — automatically archived at end-of-life, with a permanent index of what was held and why it was disposed.
One vault for every assurance activity — audit workpapers, ICFR test results, monitoring outputs, and regulatory submissions — retrievable in seconds, not hours
67% evidence reuse rate — a single item referenced across multiple activities, eliminating duplicate collection and version drift
Tamper-proof audit trail that satisfies external auditor, regulator, and forensic review standards — automatically generated, never manually assembled
Board and audit committee reports auto-populated from live engagement data — the CAE finalises, not compiles
Retention schedules by evidence type and jurisdiction — with automatic archiving and a permanent disposal record
© 2026 Falconry360 . All rights reserved.