
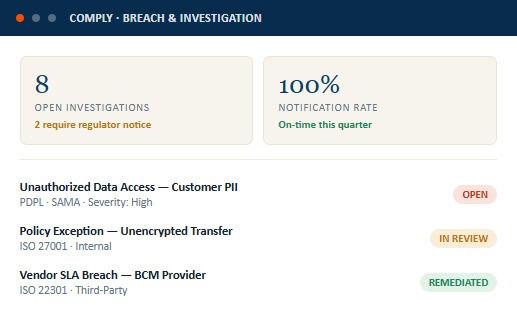
Across all severity levels
ISO, NIST, SAMA, NCA, PDPL & more
↓ 3 days vs prior quarter
Controls shared across 2+ frameworks
On-time regulator notifications
Requirements mapped to a control
With root cause documented
Requirements without a control
From first detection to regulator notification to root cause closure — every step logged, owned, and auditable.
Capture every breach or compliance violation with a consistent taxonomy — type, severity, regulatory classification, and affected scope.
Assign investigators, manage timelines, record interview notes, and collect evidence — with a full, tamper-evident audit trail.
Auto-trigger the right notification workflow — PDPL 72-hour, SAMA breach reporting, NCA incident — the moment a breach is classified.
Falconry360 turns the most stressful compliance event into a structured, documented, and defensible process.
Log and classify every compliance breach — by severity, regulatory applicability, and affected domain — to immediately route the right notification workflow.
Open a structured investigation, assign investigators, capture interview records, log evidence, and manage timelines — with an immutable audit trail throughout.
Auto-trigger regulator-specific notification sequences — PDPL 72-hour data breach notices, SAMA incident reports, NCA cyber incident disclosures — the moment a breach is classified.
Convert investigation findings into owned remediation tasks, track progress against committed dates, and close with documented root cause and preventive action.
Maintain a complete, timestamped record of all regulator correspondence related to a breach — notices sent, responses received, commitments made — in one place.
Identify patterns across breach history — by type, department, control owner — to inform the preventive control improvements your board needs to see.
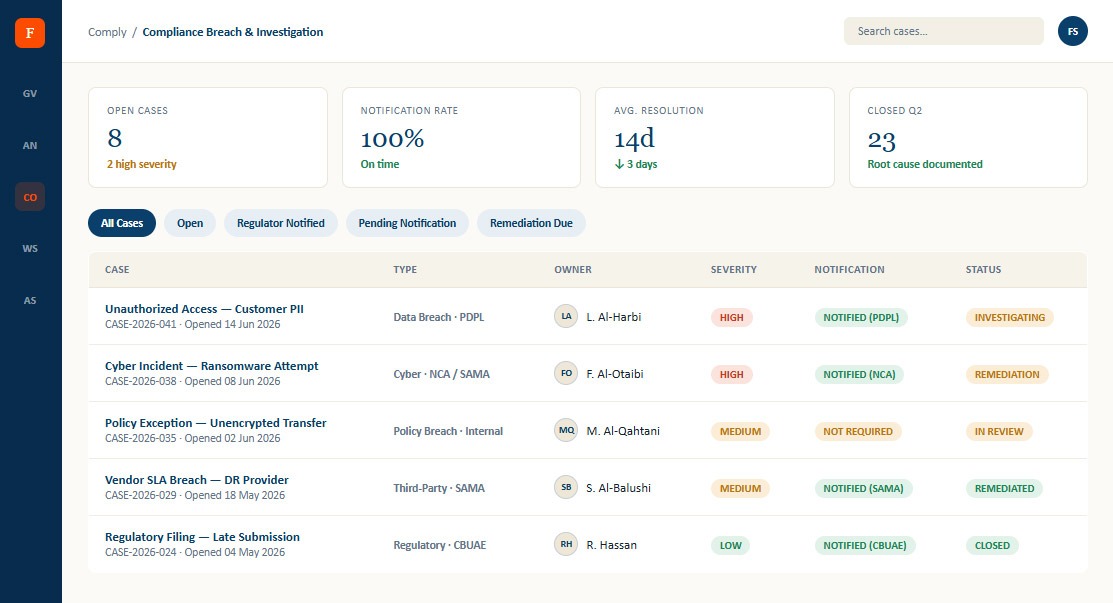
Three screens — the case register your compliance team manages, the investigation workspace your lead investigator works in, and the notification log your regulators and auditors review.
Every open and closed case — its severity, regulatory classification, notification status, and resolution timeline — in one managed view.
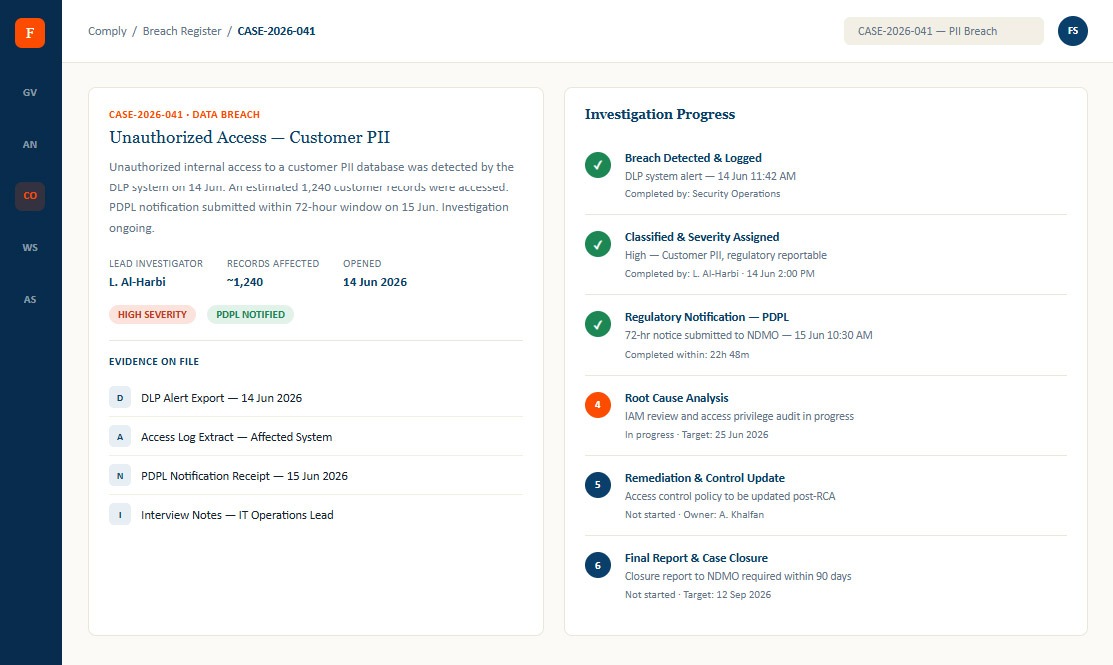
A structured investigation record — timeline, evidence, findings, and notification status — for a single high-severity breach case.
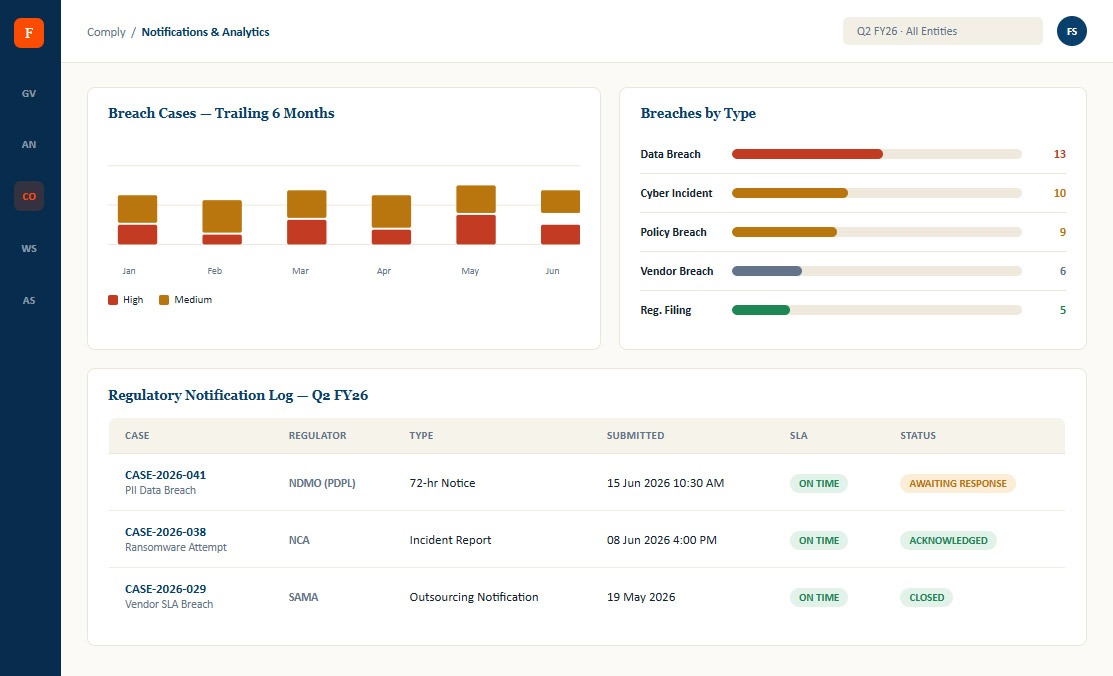
A complete log of all regulator notifications, plus trend analysis your board and audit committee need to see.
Log the breach immediately — manually, via email, or from an integrated alert — with a consistent classification taxonomy.
Determine severity, regulatory applicability, and scope. Assign a lead investigator with SLA-bound acknowledgment.
Auto-trigger the right notification within the required window — 72 hours for PDPL, same-day for NCA cyber incidents.
Gather evidence, document findings, and convert outcomes into remediation tasks with owners and deadlines.
Close the case with documented root cause, submit the final report to the regulator, and add to the breach trend log.
Structured case management that keeps investigations on track under pressure
Regulatory notification SLA tracking — 72-hr, 24-hr, and same-day obligations managed automatically
Immutable investigation audit trail that holds up to regulator scrutiny
Breach trend analysis that informs control investment decisions
FalconryX-assisted root cause analysis and control improvement recommendations
© 2026 Falconry360 . All rights reserved.