
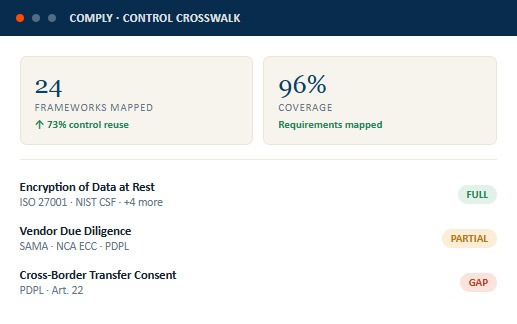
ISO, NIST, SAMA, NCA, PDPL & more
Controls shared across 2+ frameworks
Requirements mapped to a control
Requirements without a control
Stop rebuilding the same control for every new regulation. Map it once and let the crosswalk do the translation.
Maintain one structured set of controls instead of a duplicate set for every framework you adopt.
See exactly which clause, article, or sub-control each control satisfies — framework by framework, scored by mapping strength.
Update a control once — its status, owner, and evidence propagate to every framework it's mapped to.
Falconry360 treats overlapping frameworks as one mapping problem to solve well — not five separate compliance projects running in parallel.
Define each control once, then map it to every regulation, standard, or framework it satisfies — instead of recreating it framework by framework.
Build defensible crosswalks between ISO, NIST, SAMA, NCA, PDPL, PCI DSS, and more, with a documented relationship type and mapping strength for every link.
See instantly where a framework's requirements lack an equivalent control, and where one control already does the work of five.
Attach evidence once; it's automatically available to every framework requirement that control satisfies — no re-collecting the same artifact for five separate audits.
Identify duplicate and overlapping controls across frameworks, and consolidate them into fewer, better-owned controls.
When a framework is updated or reissued, see exactly which mapped controls are affected before the new version takes effect.
Three connected screens — the crosswalk matrix your compliance team builds from, the control detail your auditors drill into, and the coverage dashboard your CCO reports from.
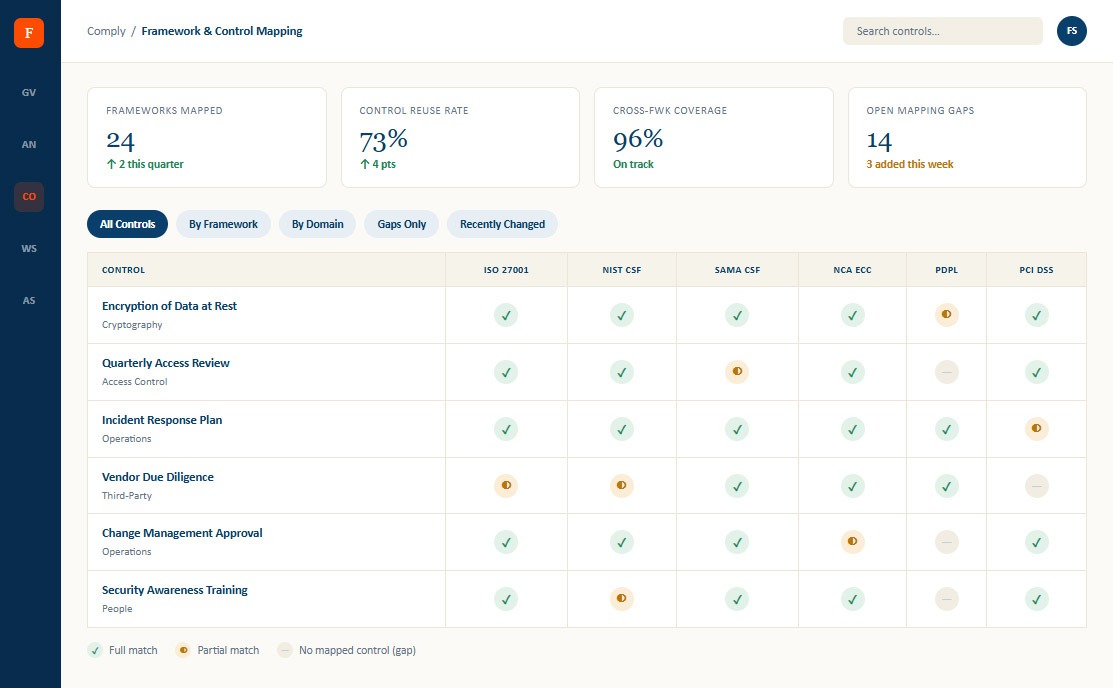
Every control plotted against every framework it satisfies — full match, partial match, or gap — at a glance.
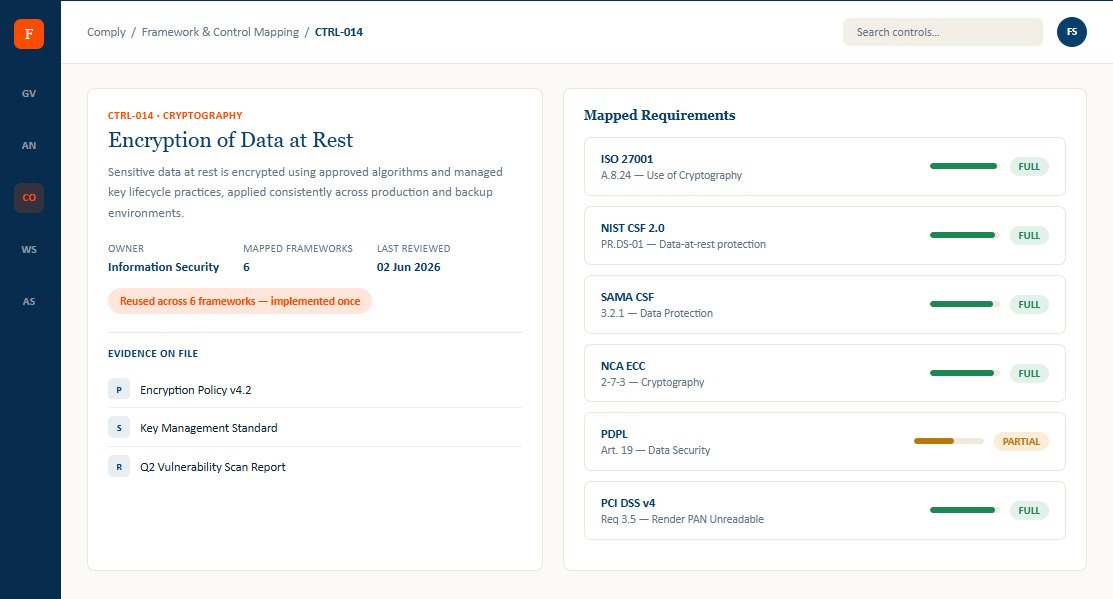
Drill into a single control to see every clause it satisfies, its mapping strength, and the evidence already on file.
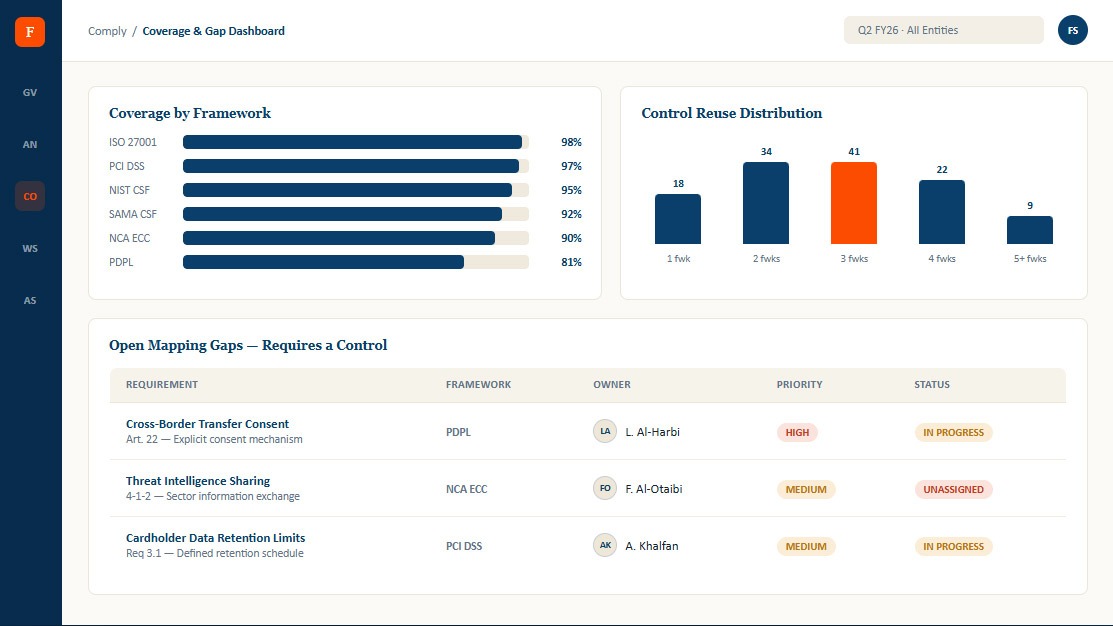
The view your CCO opens before a board meeting: coverage by framework, control reuse, and the gaps still open.
Choose the regulations, standards, and frameworks in scope for your organization.
Define each control once, written to satisfy its strictest applicable requirement.
Link every control to the clauses it satisfies, with a documented relationship type and strength.
Track mapped, partial, and unmapped requirements across every framework, continuously.
Re-map flagged controls automatically when a framework is updated or reissued.
One control library, mapped to every framework you operate under
Defensible, scored crosswalks — not best-guess equivalence
Evidence collected once, reused everywhere it applies
Instant visibility into coverage gaps before an auditor finds them
FalconryX-assisted mapping suggestions as new frameworks are added
© 2026 Falconry360 . All rights reserved.