
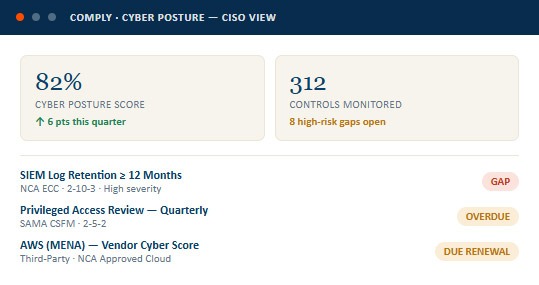
NCA, NIST, ISO, SAMA, PCI, PDPL
Across all frameworks
Material outsourcing relationships
With assigned remediation owners
One platform to test controls, evidence compliance across every applicable framework, score your vendors, and report posture to the board without translating technical findings into PowerPoint.
Test once, satisfy NCA ECC, NIST CSF, ISO 27001, and SAMA CSFM simultaneously — with scored crosswalks showing exactly where each control satisfies which requirement.
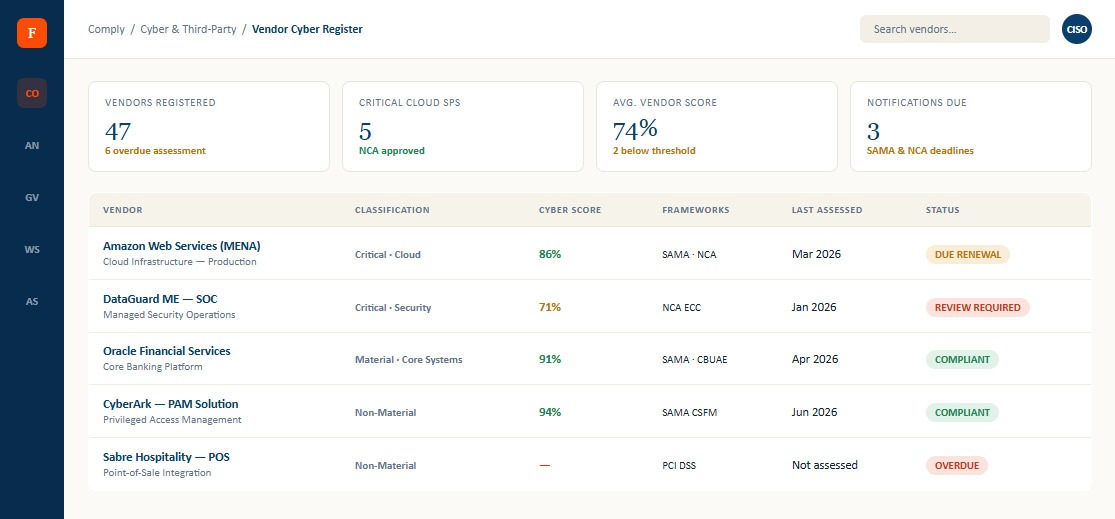
Assess every material vendor against your cyber requirements. Automated scoring, renewal tracking, and NCA outsourcing notification workflows — all in one register.
Translate technical posture into executive language. Posture scores, framework coverage, vendor risk, and open gap remediation — formatted for the board, not the SOC.
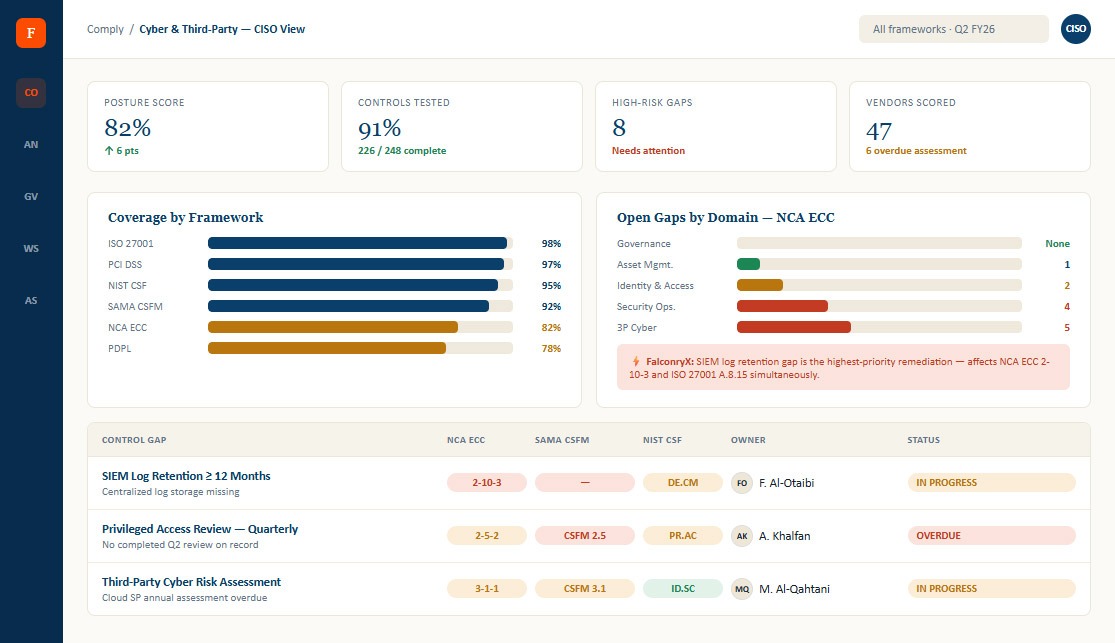
Two screens — the multi-framework cyber posture dashboard you operate from, and the vendor cyber register your team maintains.
One dashboard showing posture score, control gaps, and coverage gaps across NCA ECC, NIST CSF, ISO 27001, and SAMA CSFM simultaneously — with a FalconryX prioritised remediation queue.
Every vendor cyber assessment — classification, last score, assessment status, and regulatory notification obligations — in one managed register.
Test a control once and see where it satisfies NCA ECC, NIST CSF, SAMA CSFM, and ISO 27001 at the same time — without maintaining four separate compliance programmes.
Third-party assessments aren't a separate process — they feed directly into your outsourcing compliance obligations and NCA/SAMA notification workflows.
When a cyber incident occurs, the response workflow, notification timelines, and evidence are documented automatically — ready for NCA and SAMA scrutiny.
Automated board cyber reports that show posture score, trend, vendor risk, and key gaps — without the CISO manually converting technical findings into PowerPoint.
The core cyber posture and vendor risk module the CISO operates from daily.
Multi-framework crosswalks connecting every control to the clauses it satisfies.
Cyber incident case management with regulator notification SLA tracking.
Cyber risk register and threat intelligence feeding the enterprise risk view.
© 2026 Falconry360 . All rights reserved.