Falconry360 gives Chief GRC Officers one governed environment to connect obligations, risks, controls, evidence, ownership and remediation — with executive visibility across the organisation.
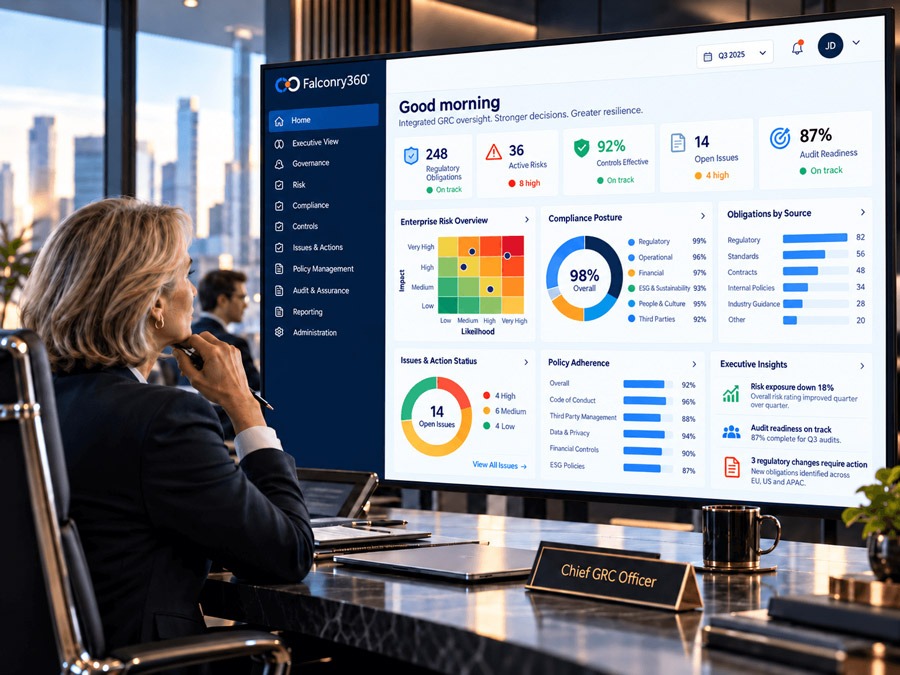
Governance, risk, compliance and assurance in one operating picture.
Ownership, due dates and remediation tracked without separate registers.
Obligation to risk, control, evidence, finding and action.
Decision-ready reporting built from governed source records.
See the full GRC position without asking each function to rebuild the story. Falconry360 connects the same governed records across teams and presents what needs attention, who owns it and what happens next.
Bring obligations, risks, controls, policies, issues and assurance into one environment with shared ownership and consistent data.
Follow a regulatory or policy requirement through the risks, controls, evidence, testing and actions that support it.
Assign owners, due dates and remediation actions across functions with clear escalation and management visibility.
A management view for enterprise GRC oversight, paired with traceability that shows how obligations, controls, evidence and actions connect.
A single executive view of regulatory obligations, enterprise risks, control effectiveness, open issues and audit readiness — with drill-down when detail is needed.
Regulatory or internal requirement
Linked exposure and impact
Mapped preventive or detective control
Supporting proof and records
Finding, owner and due date
Testing and management conclusion
Connect the governance chain once and reuse it across compliance, risk and assurance workflows — reducing duplicate registers and repeated evidence.
Governance, risk, compliance and assurance draw from the same governed data foundation instead of being reconciled manually.
Risks, controls, obligations, evidence and issues are linked once and reused across modules and reporting.
Owners, due dates, decisions and remediation remain visible from executive reporting through to operational action.
Surface regulatory impacts, risk signals and executive-ready insight while keeping source records and accountability visible.
Centralize obligations, ownership, regulatory risk and compliance responsibilities.
Connect enterprise exposures, KRIs and risk treatment to the wider GRC position.
Link policies, approvals, attestations and internal requirements to controls and obligations.
Bring assurance findings, evidence and corrective actions into the same management view.
See how Falconry360 can connect governance, risk, compliance and assurance across your organisation.
© 2026 Falconry360. All rights reserved.
Falconry360 is operated by Falconry Ltd and its affiliates, as applicable.