
Falconry Completes UAE Cybersecurity Assurance Review
Falconry completed an independent cybersecurity posture review for a major UAE environmental services organization, providing a shareholder-level view of governance, control maturity and material cyber risk exposure. The assignment was performed from an ownership and assurance perspective rather than as a detailed technology implementation. This required a concise, decision-focused view of whether cybersecurity governance and controls were sufficiently mature, where material risks existed and which issues required management attention. Falconry assessed cybersecurity governance, control maturity and key risk exposures, considered alignment with UAE national cybersecurity expectations and recognized control frameworks, and translated the findings into executive-level assurance observations and recommendations. The review provided stakeholders with a clearer independent view of the organization’s cyber posture and priority areas for follow-up. It also demonstrated how cybersecurity assessments can be tailored for boards, shareholders and portfolio owners who need assurance over material exposure without losing sight of practical remediation priorities.
Falconry Completes Oman Cyber Resilience Programme
Falconry completed a cybersecurity governance and operational resilience engagement for one of Oman’s largest energy operators, supporting a clearer view of cyber risk, control maturity and continuity readiness across a critical operating environment. The engagement reviewed cybersecurity governance, the control environment and risk-management practices, with alignment to ISO/IEC 27001 and NIST-aligned expectations. It also considered business continuity, crisis and recovery arrangements to understand how cyber and operational resilience capabilities worked together around critical operations. Falconry identified governance, technology and process gaps, assessed key dependencies and developed a prioritized, risk-led improvement roadmap. The approach was designed to move beyond a simple compliance checklist by focusing management attention on the issues with the greatest impact on resilience and sustainable maturity. The result was a more governed and implementation-focused view of the organization’s cyber and resilience posture, giving management a clearer basis for prioritizing improvement actions and strengthening continuous assurance.
Falconry Completes Oman FinTech Resilience Programme
Falconry completed a cybersecurity and business continuity engagement for one of Oman’s leading digital payments providers, supporting the organization in strengthening security governance and operational resilience in a fast-moving financial technology environment. Digital payments businesses operate with high expectations around availability, trust, information security and continuity. The engagement therefore brought together two closely connected priorities: strengthening the organization’s information security management approach and ensuring that business continuity arrangements were documented, governed and ready to support critical operations. Falconry supported the development and consolidation of cybersecurity and ISO/IEC 27001-related governance documentation alongside business continuity policies and supporting materials. The work also helped create a clearer management view of the organization’s security and resilience responsibilities and provided consolidated handbooks to support internal review and approval. The engagement demonstrated the value of treating cyber risk and business continuity as connected disciplines. For digital businesses, resilience depends not only on preventive controls, but also on clear ownership, documented response arrangements and the ability to continue critical services when disruption occurs.
Falconry Supports Saudi ISO 27001 Implementation
Falconry has supported a leading Saudi apparel company with the implementation of an information security management system aligned with ISO/IEC 27001. As organizations expand their digital operations, customer channels, internal systems and third-party dependencies, information security needs to be managed through a clear governance framework rather than isolated technical controls. ISO/IEC 27001 provides a structured basis for connecting security risks, responsibilities, policies and controls within a managed system. Falconry’s engagement supported the organization in establishing the governance and implementation foundation required for an ISO 27001-aligned information security management system. The work focused on translating security requirements into practical organizational responsibilities, documented controls and a repeatable approach to managing information security risk. The programme provides a stronger basis for ongoing security management and assurance, helping the organization maintain visibility over its information security obligations as the business and its technology environment continue to grow.
Falconry Supports Saudi NCA Implementation
Falconry has supported a major PIF-backed tourism and destination development company in Saudi Arabia with the implementation of National Cybersecurity Authority requirements as part of its broader cybersecurity maturity journey. Large development organizations operate across expanding digital environments, multiple stakeholders and a growing ecosystem of service providers. In that context, regulatory cybersecurity requirements need to be translated into practical governance, accountable control ownership and evidence that can be sustained as the organization evolves. The engagement supported the implementation of applicable NCA cybersecurity requirements through structured governance, control alignment, remediation coordination and evidence-focused execution. Falconry worked with relevant stakeholders to help turn regulatory expectations into an actionable implementation programme and strengthen visibility over progress, responsibilities and priority gaps. The programme supports a more consistent cybersecurity operating model and provides a stronger foundation for ongoing assurance, management oversight and future maturity improvement as the organization continues to scale.
Omani Advisory Firm Engages Falconry for vCISO
Falconry has supported a leading audit and advisory firm in Oman through a virtual Chief Information Security Officer model designed to strengthen cybersecurity leadership, governance and management oversight. Professional services organizations handle sensitive client, financial and corporate information while operating across increasingly digital working environments. Maintaining an effective security programme therefore requires ongoing leadership and prioritization, not only periodic technical assessments. Through the vCISO engagement, Falconry provides senior cybersecurity guidance that helps management structure security priorities, maintain governance focus, coordinate risk and control activities and keep cybersecurity visible at the appropriate decision-making level. The model gives the organization access to experienced security leadership without requiring a full-time in-house CISO position. The engagement is designed to help cybersecurity operate as a managed business capability – with clearer direction, stronger accountability and a more consistent connection between security risks, management priorities and ongoing improvement actions.
Professional Services Firm Strengthens Cybersecurity Governance Through Ongoing vCISO Support
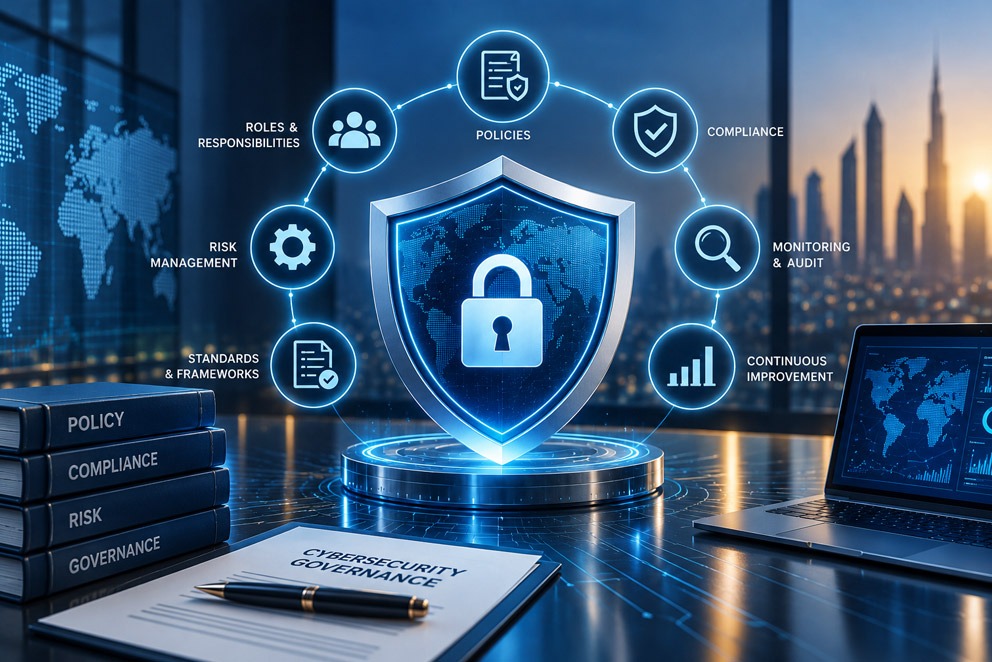
Falconry provides virtual Chief Information Security Officer support to a member firm of a global professional services network, helping strengthen cybersecurity governance, leadership and oversight on an ongoing basis. For professional services firms, cybersecurity is closely tied to client trust, regulatory expectations and the protection of sensitive business information. A vCISO model provides access to senior security leadership while allowing the organization to scale specialist input around its risk profile and priorities. Falconry’s support provides a structured leadership layer for the cyber programme, helping management prioritize risks, maintain governance focus, coordinate security initiatives and track improvement activities. The engagement also supports continuity between strategic direction and the day-to-day actions required to strengthen the organization’s security posture over time. The model demonstrates how organizations can access experienced cybersecurity leadership as a managed capability – creating clearer ownership and decision support without the dependency on a single full-time role.