Governance, risk and compliance on one record.
FalconryGRC helps boards, CROs and compliance leaders work from the same governed record—connecting accountability, risk, obligations, controls, evidence, remediation and assurance in one operating environment.
Request DemoThe issue is not information. The issue is that the information does not connect.
Risk, compliance, controls, evidence, remediation and assurance are often managed in separate registers by different teams. Leadership then receives summaries that sit outside the source record—slowing decisions and weakening traceability when a committee or regulator asks for clarity.
Multiple versions of exposure
Business, cyber, compliance and audit teams maintain overlapping views using different taxonomies, scales and owners.
Controls are duplicated
The same control is rebuilt for multiple frameworks, increasing evidence requests and creating inconsistent conclusions.
Regulatory change stays disconnected
Teams log requirements but cannot easily see downstream impact on risks, controls, evidence and accountable owners.
Reporting is rebuilt by hand
Management and board packs are assembled outside the operating data, reducing timeliness, context and trust in the story.
One record. One view. One source of accountability.
FalconryGRC is not a loose collection of registers. It sits on the Falconry360 operating model so an obligation can connect to the risks it creates, the controls that address it, the evidence that supports those controls, the issues that remain and the assurance management relies on.
From obligation to assurance—without breaking the chain.
A mature GRC environment is not a set of isolated registers. It is a relationship model that connects what the organisation must do, what could prevent it from succeeding, how those risks are controlled and how management knows the controls are working.
The same relationship model can also connect policies, business units, third parties, services, assets, KRIs, committees and reporting structures around the core governance record.
Run governance, risk and compliance as an operating system—not a reporting exercise.
Govern accountability
Structure ownership, policies, committees, approvals and decision rights around a common governance model.
Governance & policyManage enterprise risk
Maintain risk taxonomies, assessments, appetite, treatments, KRIs and reporting across entities and functions.
ERM & KRIsTranslate regulation into action
Capture obligations, assess applicability, map controls, identify gaps and maintain remediation through closure.
Regulatory complianceOperate a common control library
Reuse controls, testing and evidence across frameworks, entities and assurance activities where appropriate.
Controls & evidenceManage issues and remediation
Bring findings from risk, compliance and assurance into one accountable action environment.
Issues & actionsSee enterprise posture
Give management and boards role-based views of risk exposure, compliance, resilience, control health and unresolved actions.
Executive reportingSee the operating record behind the headline.
Move from executive posture to the underlying risks, controls, obligations, evidence and actions without leaving the governed record.

One decision view across risk, compliance and controls.
Bring material exposure, obligations, control effectiveness, resilience signals and unresolved actions into a management view without creating a separate reporting dataset.
- Risk and KRI movement
- Control effectiveness and exceptions
- Open, overdue and material actions
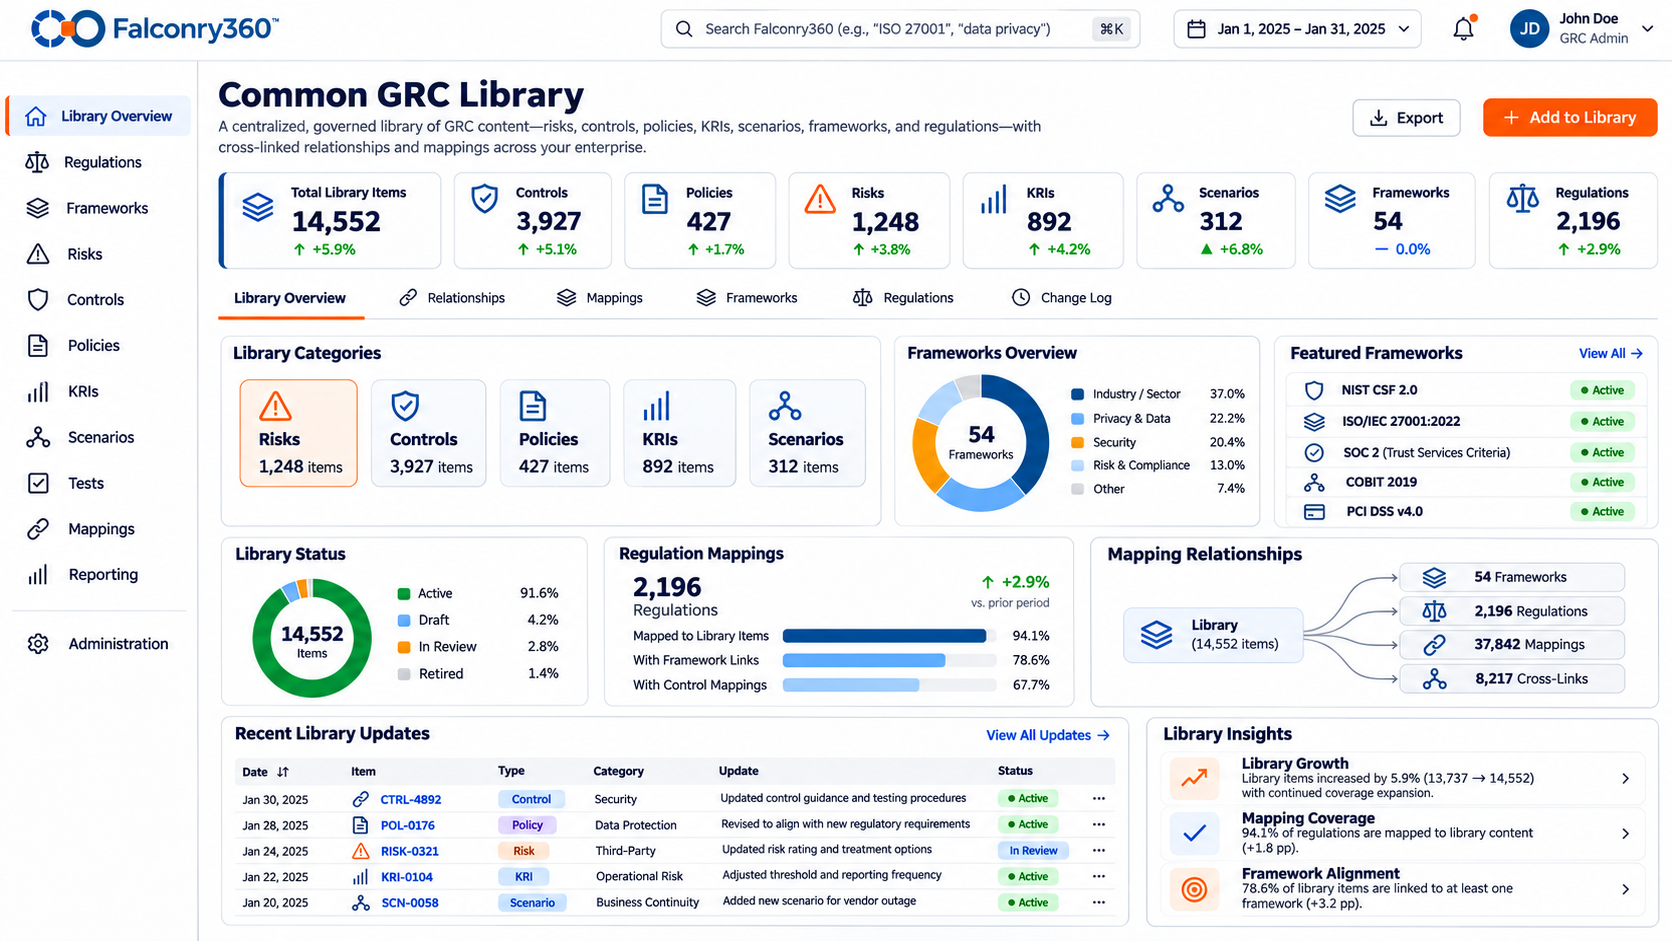
Control once. Map many.
Maintain common controls and governed relationships across regulations, risks, policies, evidence, tests and issues—reducing duplication while improving consistency.
- Many-to-many framework mapping
- Reusable evidence and testing
- Ownership, applicability and review history
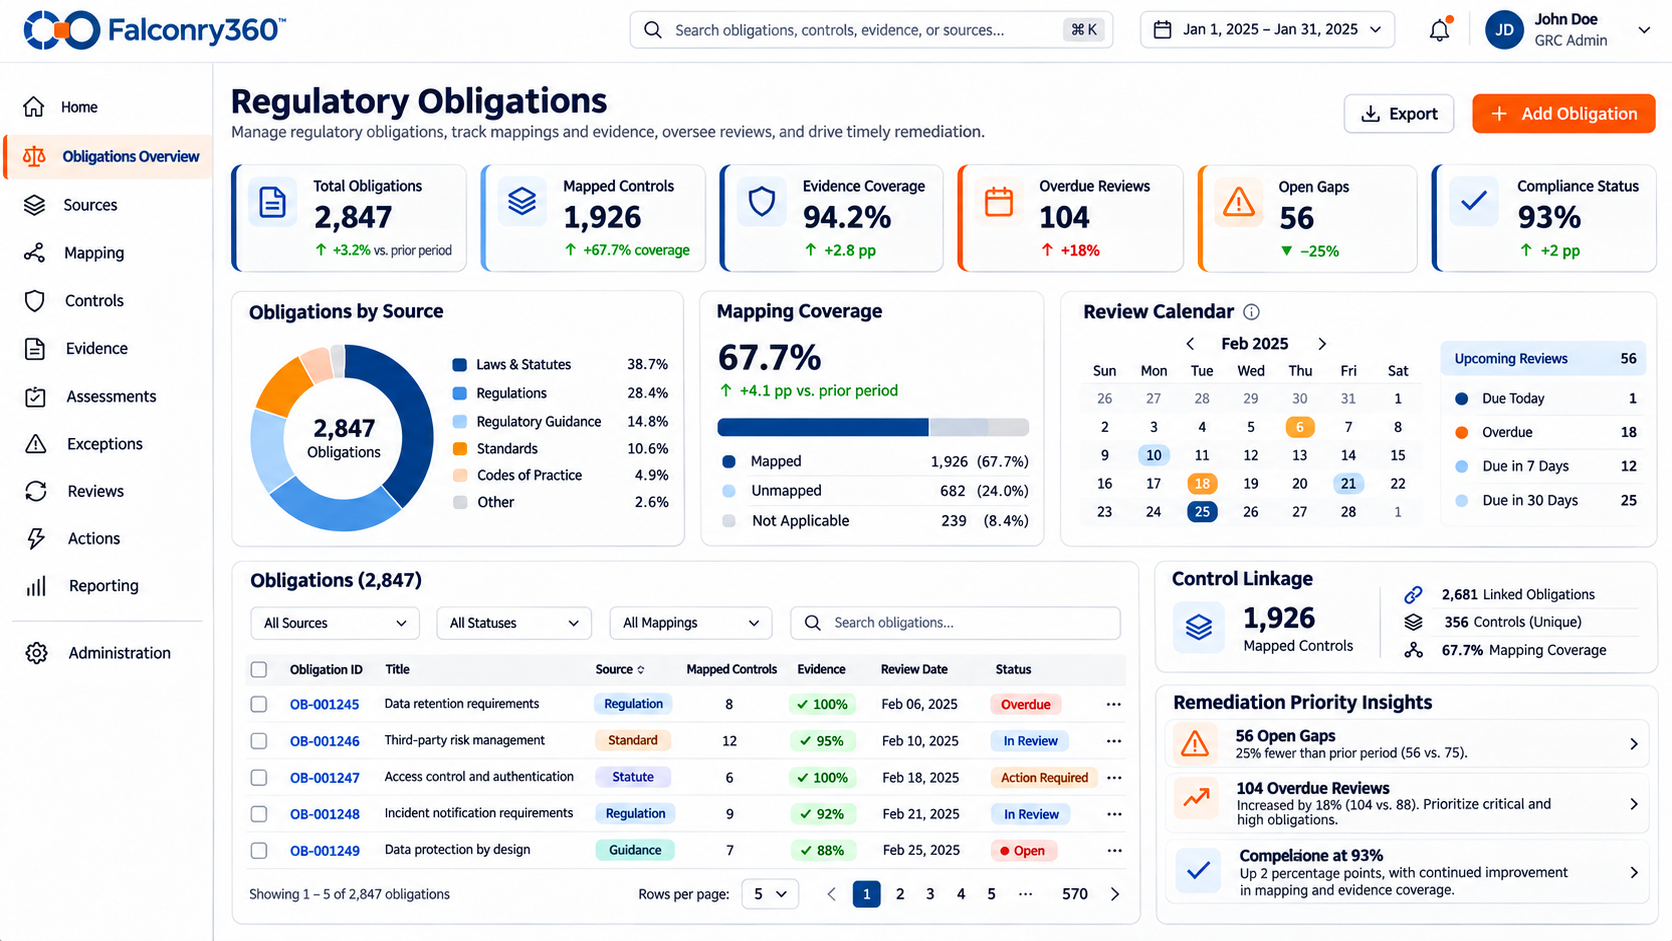
Turn regulatory requirements into controlled action.
Assess applicability, understand impact and connect changed obligations to the controls, owners and actions that need to respond—without losing sight of due dates or progress.
- Obligation ownership and status
- Requirement-to-control mapping
- Gap and remediation tracking

Keep findings accountable through closure.
Bring risk, compliance and assurance findings into the same action environment so overdue or material remediation is visible to the right level of management.
- Clear ownership and due dates
- Workflow visibility and SLA tracking
- Closure evidence and remediation history
The AI beneath every pillar.
FalconryX works across governed Falconry360 data to surface emerging exposure, map regulatory change to existing controls, identify action priorities and help draft decision-ready narratives from live records. Your people review and decide.
GRC becomes more powerful when the rest of the operating environment connects to it.
Connect FalconryGRC with the other Falconry360 propositions so risks, obligations, controls, issues and assurance inform the same enterprise view.
Use risk, controls and issues to support audit planning, testing and assurance reporting.
Connected propositionFalconryTrust →Bring cyber, privacy and digital trust risks into enterprise oversight and common remediation.
Connected propositionFalconryResilience →Connect business continuity, operational resilience and service recovery insights to GRC posture.
Connected propositionFalconryCulture →Link policies, attestations, learning and behaviour reinforcement to accountability and controls.
Connected propositionFalconryAware →Feed awareness, human-risk and participation signals into governance and risk visibility.
Connect governance, risk and controls across regional requirements and recognised frameworks.
FalconryGRC can structure obligations, risk assessments, control mappings, evidence and reporting around the governance, risk and compliance requirements relevant to your organisation. The examples below are representative rather than exhaustive.
Start with the GRC priorities that matter most.
FalconryGRC supports a broad range of governance, risk and compliance priorities. The areas below illustrate common starting points rather than defining the limits of the proposition.
Enterprise risk management
Connect appetite, assessments, KRIs, treatments and executive reporting across business units and functions.
Regulatory compliance
Manage obligations, applicability, control mapping, evidence and remediation across complex regulatory environments.
Policy & accountability
Align governance structures, policy responsibilities, approvals and ownership to the wider control environment.
Control rationalisation
Reduce duplication by operating a reusable control and evidence library across multiple frameworks and processes.
Issues & remediation
Drive coordinated action management for risk, compliance, audit and assurance findings through closure.
Management & board reporting
Move from fragmented status updates to a connected narrative grounded in governed records and live posture.
See your governance, risk and compliance environment on one record.
Explore FalconryGRC in the context of your organisation, regulatory landscape and operating model.