
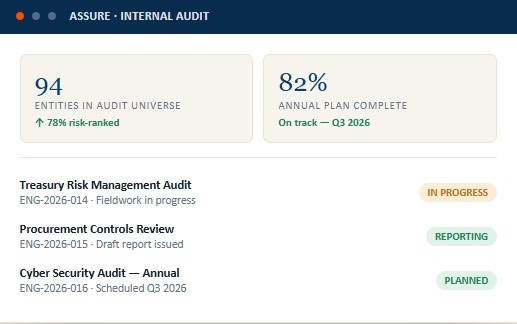
Processes, systems & business units
On track for year-end
Across 18 completed engagements
Requiring management action
From the audit universe through risk-ranked planning to engagement execution and audit committee reporting — the complete internal audit programme in one platform.
Build your annual audit plan by ranking auditable entities against live risk scores from the enterprise risk register — not a fixed rotation. Reallocate resources dynamically when the risk profile changes.
Manage each engagement end-to-end: scoping, audit programme, evidence requests, working papers, issue logging, and draft report — in a structured, reviewable workflow from open to close.
Auto-populated audit committee papers, CAE dashboards, and annual report packs — generated directly from engagement data, not manually assembled from disconnected spreadsheets.
Falconry360 meets the full spectrum of internal audit needs — from universe maintenance and risk-based planning to real-time fieldwork execution and boardroom reporting.
Define and maintain a structured inventory of all auditable entities — business units, processes, systems, and regulatory obligations — with risk ratings, last audit date, and coverage history.
Build the annual audit plan by ranking auditable entities against current risk scores from the enterprise risk register — not a fixed rotation. Reallocate resources dynamically when risk profiles change.
Manage each engagement end-to-end: scoping, audit programme, evidence requests, working papers, issue logging, and draft report — in a structured, reviewable workflow.
Maintain a secure, version-controlled workpaper library for every engagement — with structured evidence collection, reviewer sign-off, and permanent retention for external auditor reliance.
Log findings with root cause classification and management response, track corrective actions through to closure, and escalate overdue items automatically.
Real-time CAE visibility into plan completion, issue trends, resource utilisation, and engagement status — and automated audit committee papers generated from live engagement data.
Three screens — the risk-ranked audit universe your CAE plans from, the live engagement workspace your auditors execute in, and the analytics dashboard your audit committee reviews.
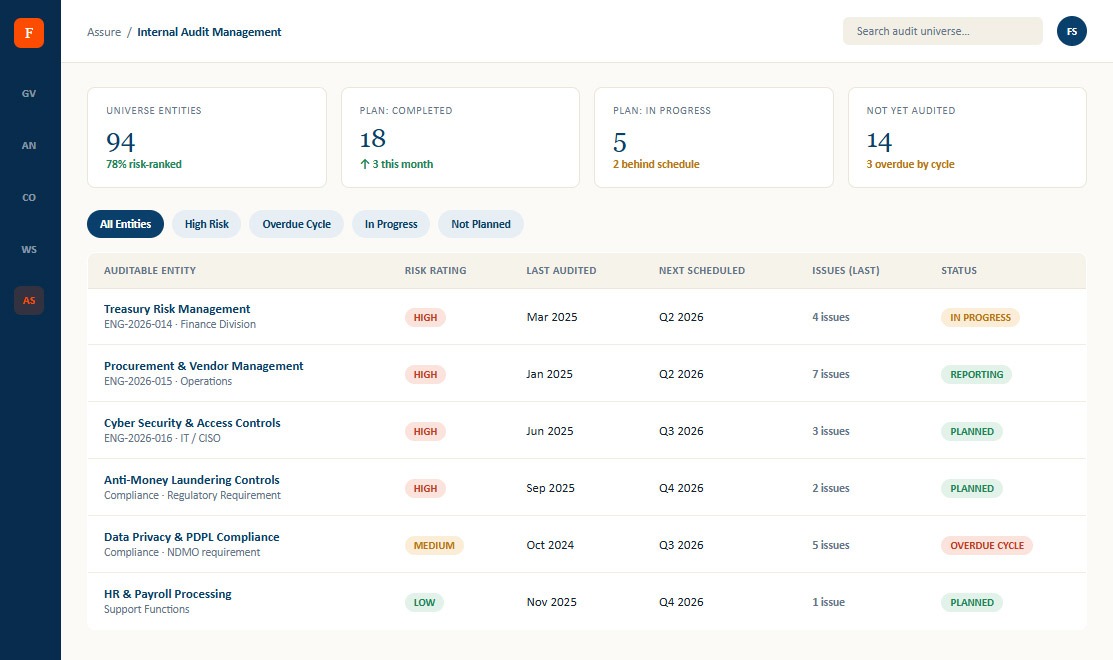
Every auditable entity — risk-ranked, with last audit date, next scheduled, coverage status, and the risk rationale for its position in the plan.
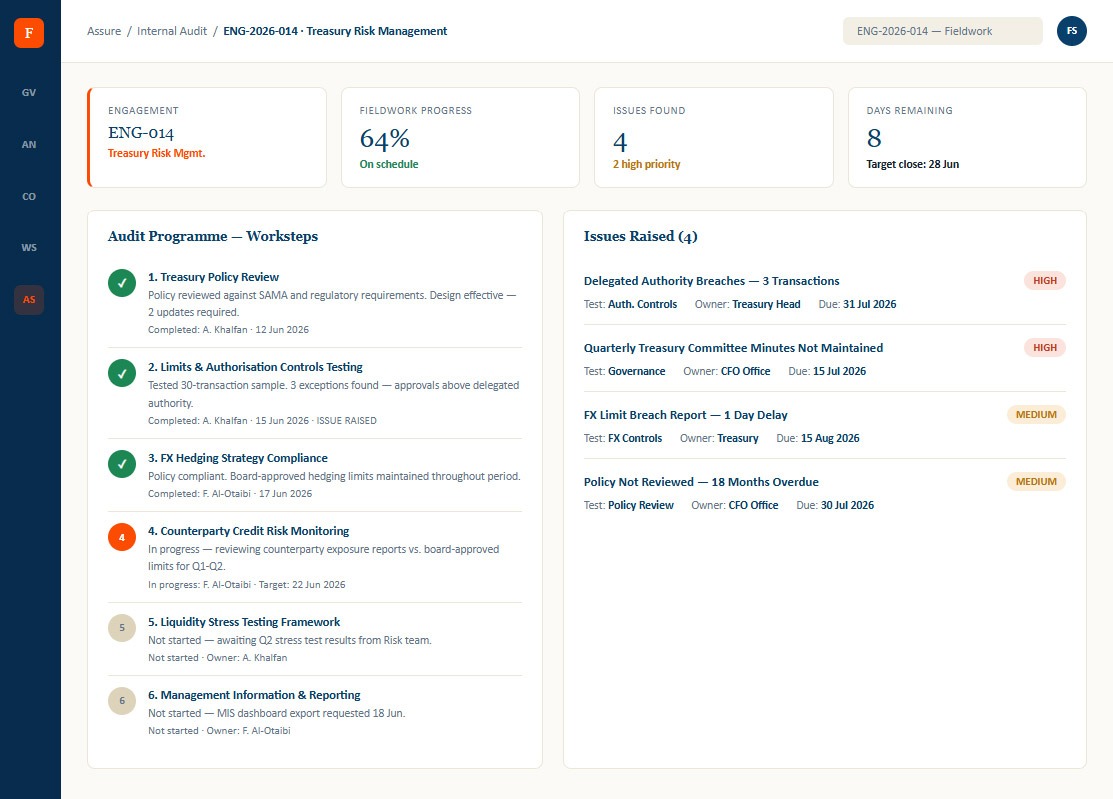
A live engagement record — fieldwork progress, open worksteps, issues logged, and evidence status — all in one view for the engagement lead.
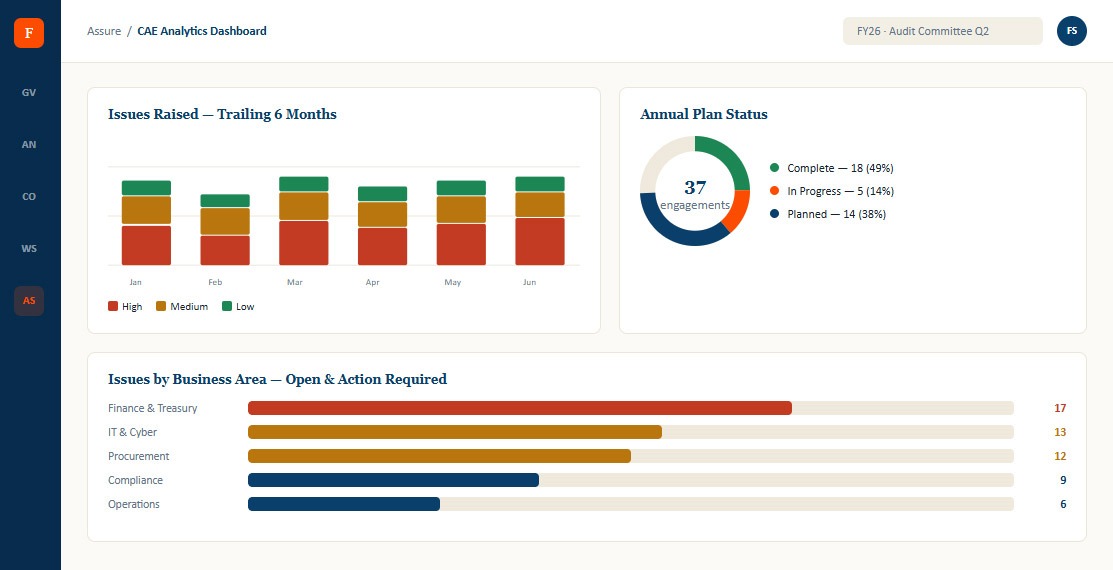
Plan completion, issue severity trends, and time budget — the view your Chief Audit Executive presents to the audit committee each quarter.
Capture all auditable entities — processes, systems, business units, regulatory obligations — linked to risk categories and last audit history.
Score each entity against the risk register and build the annual plan, allocating audit resource to highest-risk areas first.
Run scoping, fieldwork, evidence collection, and issue logging through structured worksteps — tracked in real time by the engagement lead.
Generate the draft engagement report from fieldwork data, manage management responses, and issue the final report through a defined approval workflow.
Monitor management action plans to closure, escalate overdue items, and report issue trends to the audit committee each quarter.
IIA Standards–aligned engagement lifecycle — from planning through to report issuance
Risk-based planning connected directly to the enterprise risk register — not a fixed rotation
Engagement workpapers and evidence managed in one place — with external auditor reliance package generated automatically
Audit committee reporting auto-generated from live fieldwork data — not assembled from Excel the night before
FalconryX-assisted risk scoring and sampling recommendations across large audit populations
© 2026 Falconry360 . All rights reserved.