
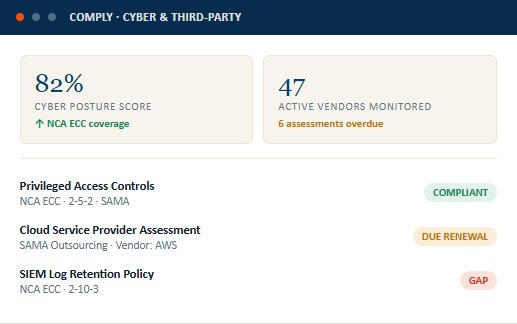
Across NCA, SAMA, NIST
ISO, NIST, SAMA, NCA, PDPL & more
↑ 6 pts this quarter
Controls shared across 2+ frameworks
Material outsourcing relationships
Requirements mapped to a control
With remediation owners
Requirements without a control
Regulators treat cyber risk and third-party risk as one exposure surface. Falconry360 manages them together.
Test cybersecurity controls against NCA ECC, SAMA CSFM, and NIST CSF requirements — continuously, not just before an audit.
Link vendor assessments directly to the outsourcing compliance obligations they satisfy — SAMA, CBUAE, and NCA notifications included.
One report to leadership showing cyber compliance and vendor risk side by side — from the same underlying data.
The regulatory expectation is clear: cybersecurity posture and outsourcing risk are not separate disciplines. Falconry360 reflects that in how it works.
Test controls against NCA ECC, SAMA CSFM, NIST CSF, and ISO 27001 simultaneously — score maturity, identify gaps, and assign remediation owners.
Conduct structured risk assessments of material outsourcing relationships, mapped to each regulator's outsourcing notification and oversight requirements.
Maintain a structured register of all material outsourcing arrangements, with automated reminders for notification, renewal, and incident reporting deadlines.
Track the ongoing compliance posture of each material vendor against contractual and regulatory requirements — with alerts when assessments lapse.
Manage regulator notification timelines for cyber incidents — SAMA 72-hour, NCA, and sector-specific obligations — with automated escalation and audit trail.
Produce regulator-ready cyber posture reports and outsourcing compliance summaries from a single data source — no manual compilation.
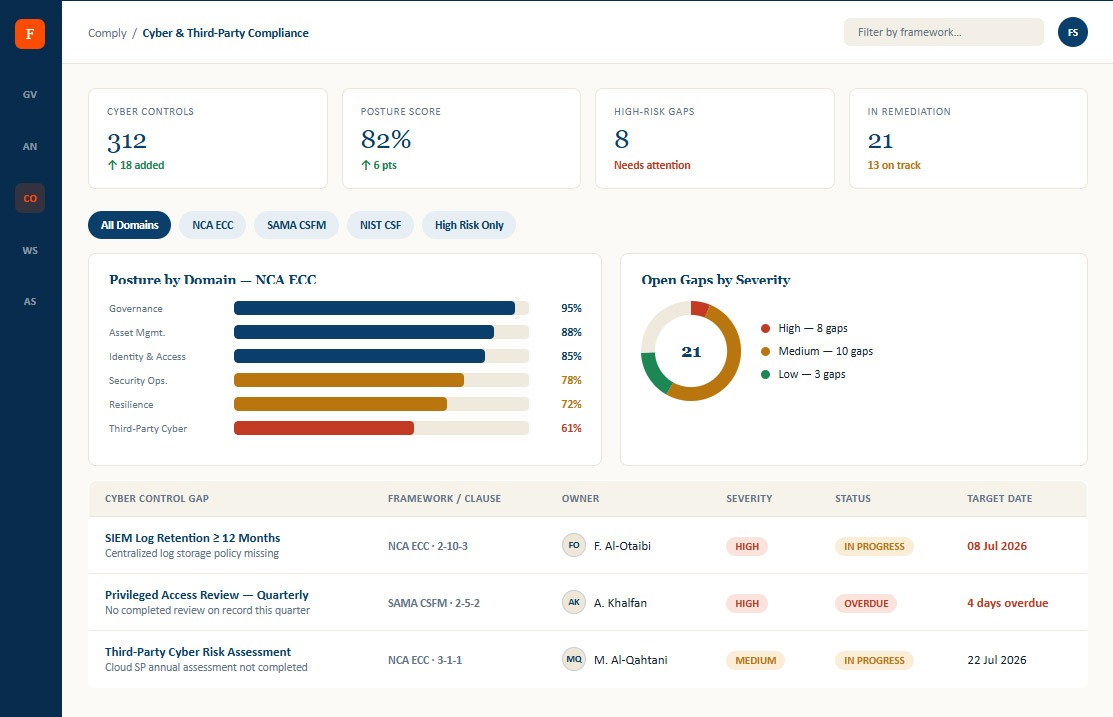
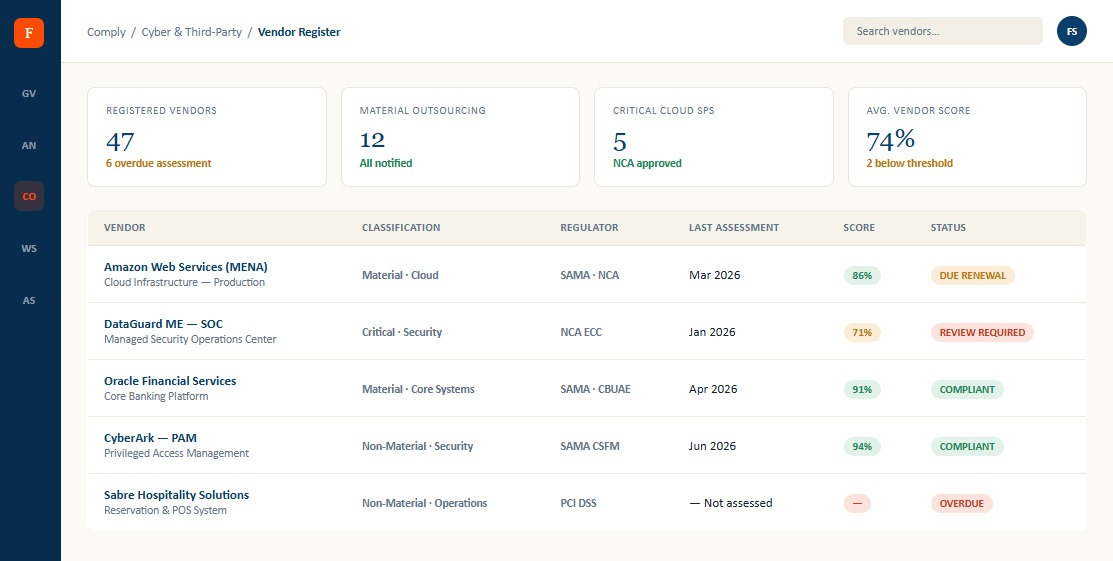
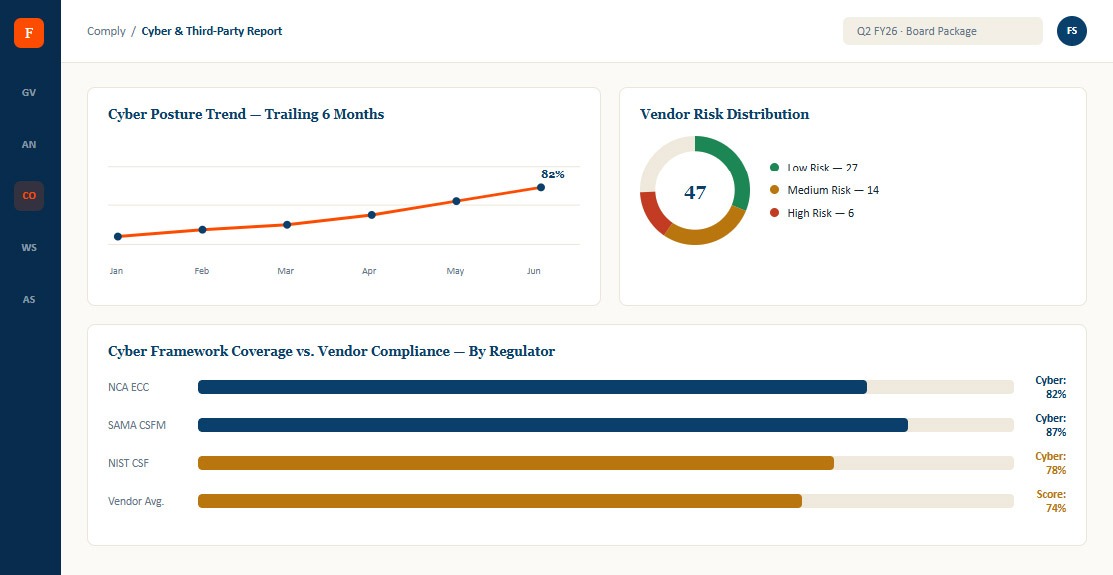
Three screens — the cyber control dashboard your CISO uses, the vendor compliance register your second line manages, and the unified report your regulator receives.
Live posture scoring against NCA ECC, SAMA CSFM, and NIST CSF — by domain, with gap owners and remediation status.
Every material outsourcing relationship — its regulatory classification, assessment status, and current compliance posture — with notification deadlines tracked automatically.
The view your CCO and CISO present to the board and regulators — cyber posture and vendor compliance in one integrated report.
Map your in-scope systems, data, and operations to the applicable cyber frameworks and regulator expectations.
Route to the accountable owner and a named backup, with SLA-bound acknowledgment.
Conduct structured compliance assessments of material outsourcing relationships against regulatory requirements.
Monitor vendor renewal deadlines, notify regulators of material changes, and flag incidents requiring escalation.
Produce one integrated cyber and vendor compliance report for board, CISO, and regulators.
NCA ECC, SAMA CSFM, NIST CSF, and ISO 27001 managed in one control framework
Third-party risk and cyber controls managed as one compliance discipline
Vendor assessments linked directly to the outsourcing obligations they satisfy
Regulator notification deadlines for incidents and outsourcing changes tracked automatically
FalconryX threat-aware control scoring — posture reflects current threat landscape
© 2026 Falconry360 . All rights reserved.