
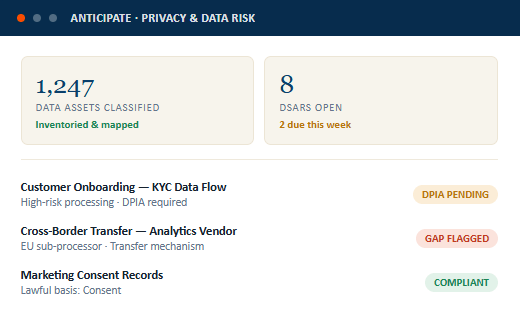
PDPL, GDPR, CCPA — one processing activity, every jurisdiction
NCA, SAMA, ISO 27001, NIST CSF & more
ISO, NIST, SAMA, NCA, PDPL & more
Access, deletion, portability, rectification
Identity, Infra, Endpoint, Data, Cloud, Third-Party
Controls shared across 2+ frameworks
Fires on high-risk processing, not a deadline scramble
CVSS · EPSS · KEV-aware prioritisation
Requirements mapped to a control
Source system to sub-processor to destination
Shared taxonomy, shared severity scale
Requirements without a control
Stop maintaining separate compliance trackers for every privacy law.
One processing activity, mapped once, satisfies PDPL, GDPR, and CCPA simultaneously.
Every processing activity — system, purpose, lawful basis, data category, recipient — lives in one register, linked to the assets and vendors it actually touches.
One processing activity, mapped to every applicable privacy law at once — so a new regulation doesn't mean a new spreadsheet.
Privacy Impact Assessments triggered automatically by high-risk processing, tracked to completion, and trended over time.
Six connected capabilities that turn scattered privacy records into one defensible, always-current programme.
Every processing activity in one register, linked to the assets and vendors it touches. No rebuilding the RoPA from scratch before every audit.
Stop maintaining separate trackers for PDPL, GDPR, and CCPA. One processing activity, mapped to every applicable law simultaneously.
Privacy Impact Assessments triggered automatically by high-risk processing — tracked to completion, trended over time, not a deadline scramble.
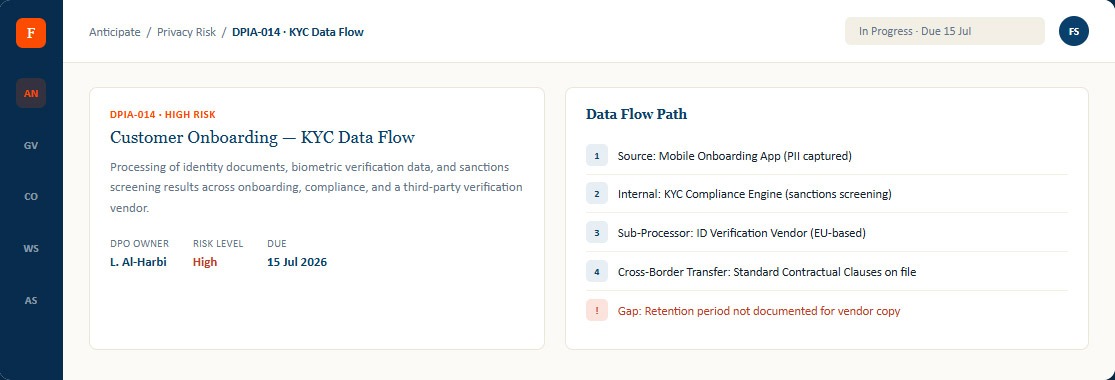
The full propagation path of personal data — source system, internal processing, sub-processors, cross-border — so every transfer mechanism is visible.
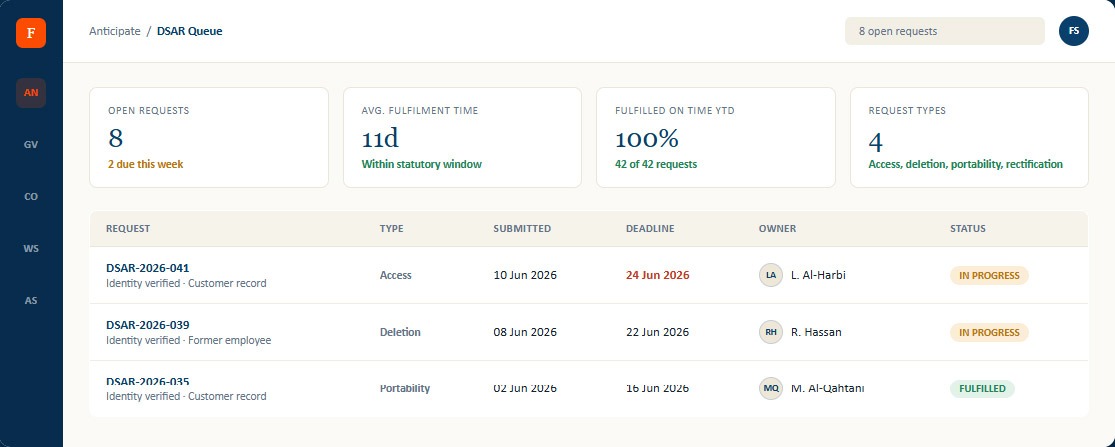
Access, deletion, portability, and rectification requests run through one queue with identity verification and a visible countdown to the statutory deadline.
PDPL readiness, DSAR performance, and processing risk tracked automatically — privacy board pack drafted with evidence already attached.
Three screens the RoPA register that updates itself, the DPIA workflow that runs on a schedule,
and the DSAR queue with a visible deadline countdown.
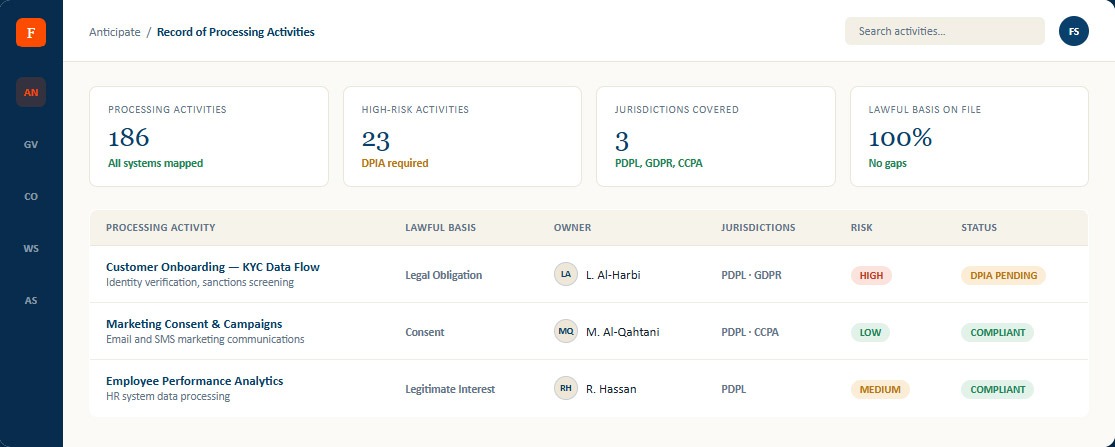
Every processing activity — system, purpose, lawful basis, data category — mapped to every applicable jurisdiction at once.
See where personal data actually goes — source system, internal processing, sub-processors, cross-border with every transfer mechanism visible.
Access, deletion, portability, and rectification requests in one queue — identity verification, fulfilment tracking, and a visible countdown to the statutory deadline.
Every processing activity captured with purpose, lawful basis, data category, and recipient — linked to the systems and vendors it touches.
One processing activity mapped to PDPL, GDPR, and CCPA simultaneously — a new regulation doesn't mean a new spreadsheet.
High-risk processing fires a DPIA automatically — tracked to completion, not chased down before a deadline.
Source system to sub-processor to cross-border destination — every transfer mechanism visible, every gap flagged.
DSARs fulfilled inside the statutory deadline, every time — with board-ready privacy reporting compiled automatically.
One RoPA, mapped to every applicable privacy law — not a tracker per jurisdiction
DPIAs triggered automatically by high-risk processing — never missed, never late
Real data flow maps — where personal data actually goes, not where policy says it goes
DSARs fulfilled inside the deadline — every time, with a visible countdown, not a shared inbox
FalconryX reads your data flows, not just your policy documents — and tells the DPO what to assess first
© 2026 Falconry360 . All rights reserved.