
Tiering, due diligence, assessment, monitoring, exit
NCA, SAMA, ISO 27001, NIST CSF & more
ISO, NIST, SAMA, NCA, PDPL & more
Due diligence, security, PCI-DSS, exit
Identity, Infra, Endpoint, Data, Cloud, Third-Party
Controls shared across 2+ frameworks
Sub-processors and downstream dependencies
CVSS · EPSS · KEV-aware prioritisation
Requirements mapped to a control
Critical, material, standard, non-material
Shared taxonomy, shared severity scale
Requirements without a control
Stop rediscovering vendor risk at renewal. Tier, assess, monitor, and track every vendor — and the vendors behind your vendors — in one register.
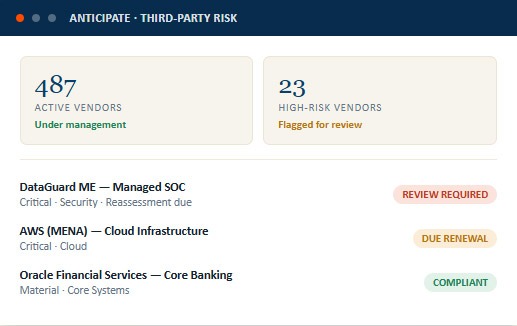
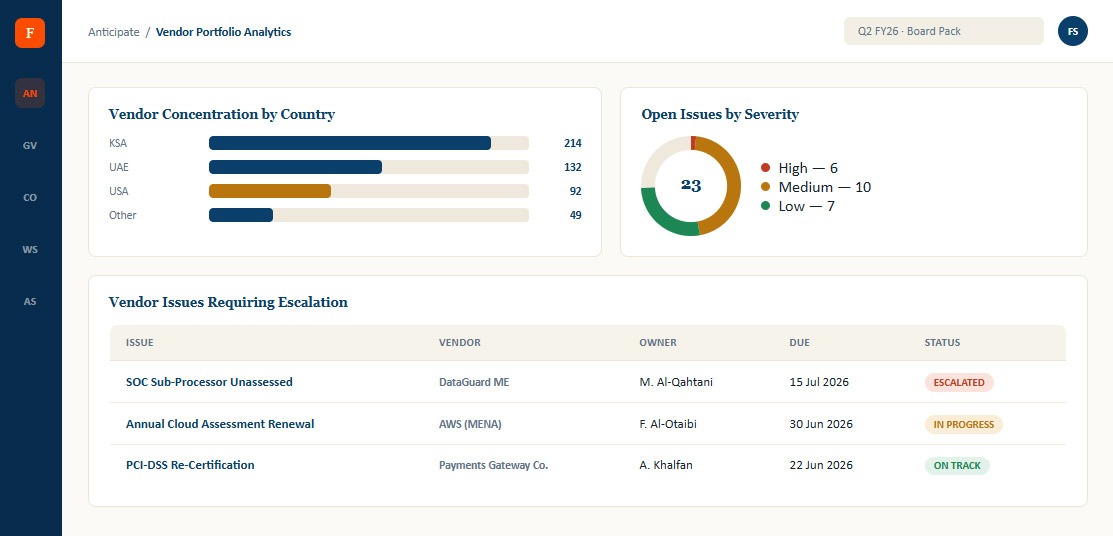
Every third party — cloud provider, payment processor, consulting partner — scored by criticality and residual exposure, with high-risk vendors surfaced automatically.
Criticality, risk tier, and residual risk tracked as three distinct fields — a critical vendor with strong controls is a different risk than one with none.
Your direct vendor is rarely the whole story. Falconry360 maps the sub-processors and downstream providers your vendors rely on.
Six connected capabilities that replace the annual questionnaire cycle with continuous, structured oversight.
Every third party — cloud provider, payment processor, consulting partner — scored by criticality and residual exposure, with high-risk vendors surfaced automatically.
Criticality, risk tier, and residual risk tracked as three distinct fields. Filter by tier, status, or country in seconds.
Falconry360 maps fourth-party dependencies — so a single point of failure doesn't take down five "unrelated" vendors at once.
Annual due diligence, security assessments, PCI-DSS reviews, and exit assessments run through the same structured workflow, with a queue showing what's due.
A finding with no remediation plan is just a paragraph in a report. Every issue becomes a tracked action with an owner, due date, and escalation path.
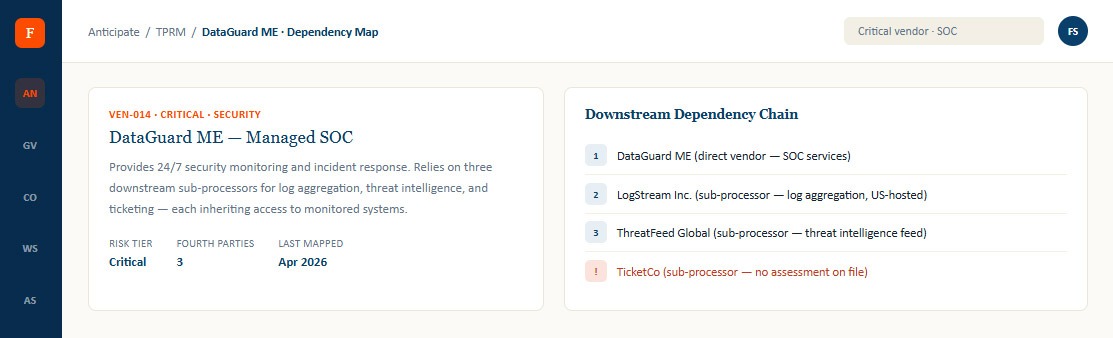
Exposure trend, concentration by type and country, and assessment throughput tracked automatically — board pack drafted with evidence attached.
Three screens — the tiered vendor register your team manages, the fourth-party dependency map that surfaces hidden risk, and the portfolio analytics the board reviews.
Every vendor scored by criticality and residual exposure, with risk tier and assessment status visible at a glance.
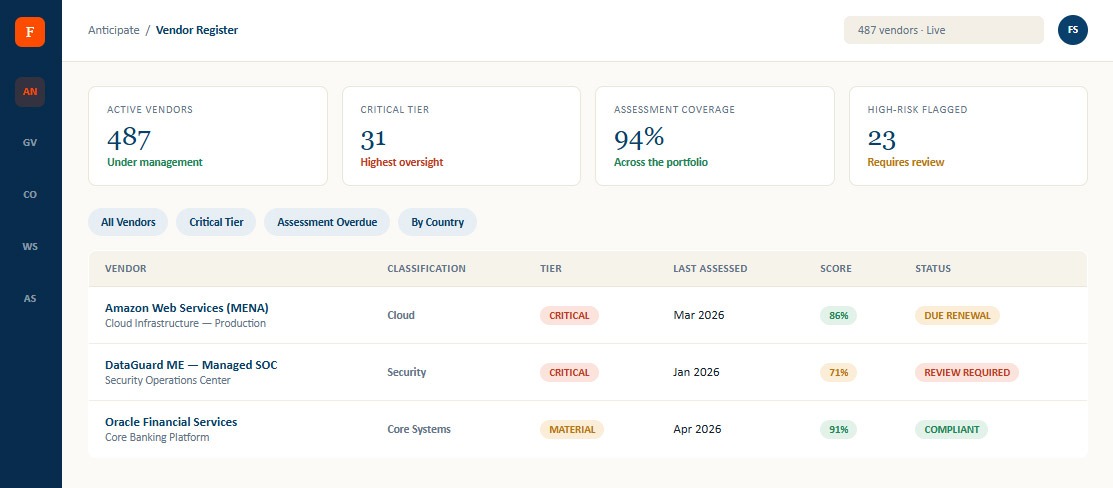
Your direct vendor is rarely the whole story. See the sub-processors and downstream providers your critical vendors rely on.
Loss trend, RCSA coverage, and KRI breaches integrated into one report — drafted automatically, evidence already attached.
Every new vendor scored by criticality and inherent risk, assigned a tier that determines the level of ongoing oversight.
Due diligence assessment run, fourth-party sub-processors mapped, so hidden concentration risk is visible from day one.
Reassessments triggered automatically by tier — annual for critical, less frequent for lower-risk vendors — never missed.
Every finding becomes a tracked action with an owner, due date, and escalation path if the vendor doesn't respond.
Exposure trend, concentration by type and country, and assessment throughput compiled automatically for the board.
One register for every vendor — not a spreadsheet per business unit
Tiered by inherent risk, not gut feel — critical vendors get the oversight they need
Fourth-party mapping surfaces the concentration risk hiding behind your direct vendors
Every issue tracked to closure with an owner, due date, and escalation path
FalconryX reads vendor posture like an analyst — at the speed of your portfolio, not one questionnaire at a time
© 2026 Falconry360 . All rights reserved.