
Governance as a Performance Enabler: Moving from Reporting to Decision Intelligence
For many organizations, “governance” still means producing reports: risk heatmaps, compliance dashboards, audit summaries, and resilience status updates. These artifacts are important, but they often arrive late, live in PowerPoint, and are disconnected from day‑to‑day decisions. Governance becomes a periodic ritual instead of a real‑time enabler of performance. The real opportunity is to treat governance not as a reporting function, but as a decision system. In that model, governance provides leaders with timely, reliable, and connected intelligence so they can take better risks, move faster, and respond confidently to regulators, customers, and crises. The Limits of Governance-as-Reporting Most governance functions were built around the need to demonstrate compliance and control. As a result, they are optimised for documentation rather than decisions. Typical symptoms include: Governance teams spending weeks assembling board and committee packs from multiple tools and spreadsheets Risk, compliance, audit, and cyber each producing their own dashboards, with different taxonomies and ratings Key decisions being made on static snapshots that are already out of date by the time they are presented In this world, governance is perceived as a cost centre and a brake on speed. It satisfies formal requirements, but it struggles to influence real business choices—such as launching products, entering markets, or changing operating models. What Decision Intelligence in Governance Looks Like Decision intelligence in governance means that information is structured, connected, and available in a way that directly supports choices leaders must make. Instead of asking, “What can we report?”, the system is designed to answer questions like: “If we launch this product or enter this market, what risks, obligations, and control gaps matter most?” “Where are we taking risks that are misaligned with our stated appetite or regulatory expectations?” “Which incidents and control failures are early signals of a bigger issue in a particular business line or region?” “What trade‑offs are we making under stress, and how do they affect our Minimum Viable Company?” To enable this, data from risk, compliance, resilience, cyber, and audit needs to live in a unified model, with clear linkages between strategy, risks, controls, obligations, incidents, and assurance outcomes. When those connections are in place, governance insights become inherently decision‑shaped rather than report‑shaped. How Governance Becomes a Performance Enabler When governance data and workflows are integrated, several shifts happen that directly support performance. From backward‑looking to forward‑looking Instead of only explaining what went wrong, governance surfaces emerging themes, risk drift, and regulatory signals early enough to adjust course. Leadership can make informed decisions before an issue becomes a loss or a breach. From one‑size‑fits‑all to context‑specific insights A single central view can be sliced by business unit, product, region, or regulator. This allows leaders to see exactly what matters for their portfolio and to compare units on risk‑adjusted performance rather than just raw volume. From friction to flow in execution When obligations, risks, and controls are linked to workflows and owners, decisions taken at the top can be translated into concrete actions, tracked to completion, and evidenced. This reduces execution risk and accelerates change. From risk avoidance to informed risk‑taking With clearer visibility of exposures and mitigations, leadership can say “yes” more often, but with conditions: proceed, provided certain controls are in place, certain thresholds are monitored, and certain scenarios are tested. In this mode, governance does not slow the business down; it gives the business a sharper edge. The Role of AI and Real‑Time Data AI and real‑time data are critical enablers of this shift from reporting to decision intelligence. AI makes sense of complexity It can help classify and cluster risks, interpret regulatory changes, suggest control mappings, and highlight patterns across incidents and assessments. This reduces noise and brings the most relevant information to the surface. Real‑time data keeps the picture current When control tests, incidents, assessments, and third‑party reviews feed into a common platform continuously, dashboards and alerts are always close to the real state of the environment. Decisions are based on living data, not last quarter’s snapshot. Narratives and recommendations become dynamic Instead of manually assembling lengthy reports, AI can draft concise, tailored narratives for different audiences—executive committees, boards, regulators—grounded in the same underlying data. Together, this turns governance from a static documentation engine into a dynamic advisory layer for the business. How Falconry360 and FalconryX Support Decision Intelligence Falconry360 is designed as a governance operating system with a single data model across its five intelligence layers: GOVERN, ANTICIPATE, COMPLY, WITHSTAND, and ASSURE. That structure is what allows decision intelligence to emerge. Strategy, policies, and AI governance in GOVERN are linked to the risks and obligations that shape them. Enterprise, cyber, privacy, and third‑party risks in ANTICIPATE are connected to controls, incidents, and business services. Regulatory obligations and changes in COMPLY map directly into actions, owners, and evidence. Resilience scenarios and MVC assumptions in WITHSTAND draw on the same assets, vendors, and risks. Assurance activities in ASSURE test the same controls and processes that management relies on. FalconryX, the embedded AI engine, then uses this connected data to provide intelligent assistance: suggesting risks, mapping regulations, spotting patterns, and drafting reports and executive summaries. Leaders can ask natural‑language questions and get answers grounded in live platform data. The result is a governance environment where: Board packs are generated from connected, always‑current data. Risk and compliance discussions focus on choices and trade‑offs, not on reconciling numbers. Regulatory interactions are supported by clear, evidence‑linked narratives. Performance conversations naturally incorporate risk, resilience, and assurance perspectives. Making the Shift in Practice Moving from governance‑as‑reporting to governance‑as‑decision‑intelligence does not require a big bang. A pragmatic approach is to: Start by centralising key libraries—risks, controls, obligations, assets, vendors—and linking them to incidents and issues. Identify a few critical decision forums (for example, product approval, investment committees, or risk committees) and design views tailored to the questions they regularly face. Introduce AI gradually to accelerate tasks that are already well understood: mapping, summarising, prioritising, and drafting. Use feedback from leadership to refine which insights are most useful, and iterate. Over time, the organization experiences governance differently. Instead of
Inside Falconry360’s Five Intelligence Layers: GOVERN, ANTICIPATE, COMPLY, WITHSTAND, ASSURE
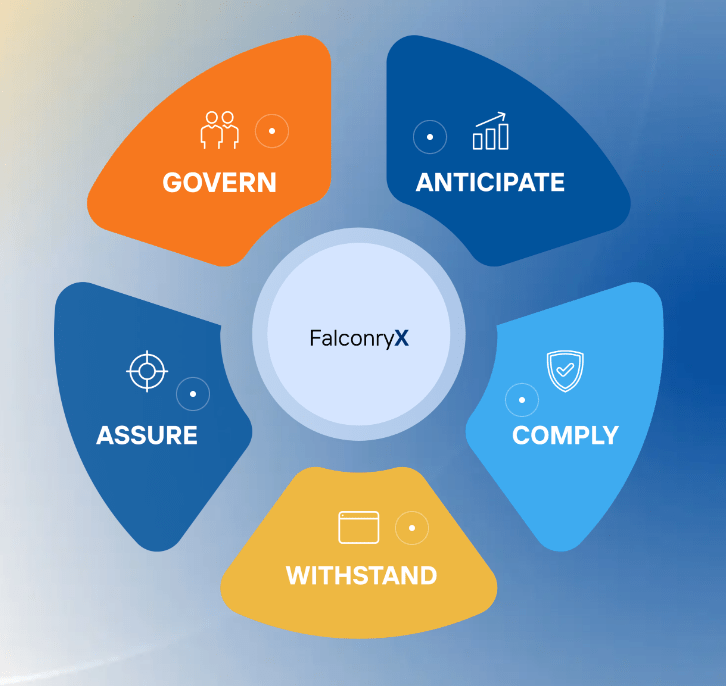
Most organizations did not design their governance environment on a whiteboard. It evolved over time: separate risk tools, standalone compliance trackers, audit systems, and a long tail of spreadsheets and emails. Each function sees its own slice of reality, but nobody sees the whole. Falconry360’s five intelligence layers are meant to fix exactly that—by structuring governance into a single, connected operating model. Instead of thinking in terms of “modules”, Falconry360 organizes governance, risk, compliance, resilience, and assurance into five layers that share the same data model, libraries, and workflows: GOVERN, ANTICIPATE, COMPLY, WITHSTAND, and ASSURE. Together, they turn fragmented activities into one integrated governance operating system. The Logic Behind the Five Layers The five layers are designed around the natural lifecycle of governance: You set direction and guardrails (GOVERN). You identify and understand risks (ANTICIPATE). You translate rules into obligations and actions (COMPLY). You prepare to absorb and survive disruption (WITHSTAND). You validate and strengthen control effectiveness (ASSURE). All of this runs on one shared data model and a set of central libraries: risks, controls, obligations, policies, assets, vendors, issues, and actions. That is what allows information to flow across layers instead of being trapped in separate systems. GOVERN – Strategic Governance Layer GOVERN is where strategy, ethics, culture, and oversight are translated into a structured operating model. It is the layer that connects “tone from the top” with how the organization actually behaves. Typical capabilities in this layer include: Strategy and performance management, aligning objectives and KPIs with risks, controls, and initiatives Policy lifecycle management, including drafting, approvals, publication, and attestations Ethics, integrity, and conduct processes, covering conflicts of interest, disclosures, and breaches Culture and learning management, linking training and awareness to real governance priorities Whistleblowing and case management, so concerns are captured, triaged, and investigated systematically AI governance, defining how AI is used, controlled, and monitored inside the organization For boards and executives, GOVERN provides a clear view of how expectations—on conduct, risk appetite, and AI use—are turned into policies, processes, and real behaviour. ANTICIPATE – Risk & Intelligence Layer ANTICIPATE is the organization’s radar. It provides integrated, near real-time visibility into risks across the enterprise so leadership can see what is coming, not just what has already happened. This layer typically covers: Enterprise risk management and central risk taxonomy Cyber and technology risk, connected to assets, vulnerabilities, and security controls Privacy and data risk, aligned with data protection laws and internal data handling rules Third-party risk management, including due diligence, onboarding, and continuous monitoring Regulatory and external risk intelligence, capturing changes in the environment that affect the risk profile FalconryX, the platform’s AI engine, plays a strong role here by: Suggesting new risks or changes in risk levels based on incidents, external signals, or control data Clustering related risks to avoid duplication and highlight systemic themes Helping prioritize risks based on impact, velocity, and control coverage ANTICIPATE is where you stop treating risk as a static register and start treating it as a living, connected view of exposure. In markets like KSA, the ANTICIPATE layer can be configured directly against NCA and SAMA CSF requirements, so cyber and technology risks are assessed and monitored against those specific control baselines. COMPLY – Regulatory Execution Layer COMPLY translates regulatory complexity into structured, executable workflows. Instead of treating laws and guidelines as documents that sit in shared drives, this layer converts them into obligations that can be owned, evidenced, and reported on. Key elements typically include: Regulatory obligations management and registers for each regulator and jurisdiction Clause-level mapping from regulations, standards, and guidance into internal controls and processes Regulatory change management, from horizon scanning through impact assessment and action tracking Supervisory reporting and exam readiness, with evidence-linked data for faster, cleaner responses Compliance risk assessments and control effectiveness reviews Incident and breach management, including notification workflows and root cause analysis FalconryX helps here by reading and summarising regulatory updates, suggesting clause mappings to existing controls, and drafting first versions of impact analyses or responses. COMPLY is where “what regulators say” becomes “what we need to do” in a structured, auditable way. WITHSTAND – Resilience Layer WITHSTAND is about ensuring the organization can continue to operate—even when critical services, suppliers, or locations are disrupted. It ties operational resilience, business continuity, and crisis management into a single view. Within this layer, organizations can: Identify important business services and map them to processes, systems, locations, people, and third parties Build and maintain business continuity and disaster recovery plans, linked directly to assets and dependencies Run crisis and incident management workflows, including escalation paths, communication plans, and decision logs Conduct crisis simulations and stress tests, capturing learnings and actions Model a Minimum Viable Company (MVC): the essential capabilities that must be preserved to keep the organization functioning during severe disruption Because WITHSTAND uses the same asset inventory, vendor registry, risk data, and control library as the rest of the platform, resilience planning is not a separate world. It reflects the same reality that risk, compliance, and audit teams see. ASSURE – Assurance & Audit Layer ASSURE provides the independent validation layer. It is where internal audit, ICFR, and combined assurance functions test whether controls are designed and operating effectively—and whether risks are truly under control. This layer supports: Risk-based audit planning that leverages live risk, control, and incident data Audit engagements where workpapers, tests, and evidence are linked directly to platform objects (risks, controls, processes, obligations) ICFR programs, including scoping, control testing, and deficiency tracking Issues and remediation management that is shared with risk and compliance, not managed in isolation Continuous monitoring and analytics, where data trends and anomalies can trigger further review Because ASSURE sits on the same data model as the rest of Falconry360, auditors no longer have to rebuild their own view of the world. They test the same risks and controls that management uses, improving trust and reducing duplication. The Power of One Shared Data Model The real strength of the five-layer architecture is not the labels. It is the fact that all layers are connected through shared libraries and
From GRC Tools to a Governance Operating System: Why the Shift Is Inevitable
Most regulated organizations are still running governance on spreadsheets, point solutions, and legacy GRC tools that were never designed for the complexity and speed of today’s risk environment. These setups capture information, but they rarely drive decisions. The result is a governance model that is slow, fragmented, and often out of sync with what boards and regulators expect. A new model is emerging: the governance operating system. Instead of being “a GRC tool” that sits on the side, it becomes the connective layer that runs strategy, risk, compliance, resilience, cyber, and assurance on a single, intelligent platform. Why Legacy GRC Is No Longer Enough Most GRC environments grew organically over years: a risk tool here, a compliance repository there, some audit software, and countless spreadsheets in between. Each does a narrow job, but together they create friction. Data is duplicated, inconsistent, and hard to reconcile. Teams spend more time preparing reports than managing risk, while boards and regulators receive delayed, static snapshots instead of live intelligence. This is not just a technology problem; it is a structural one. The way governance is architected no longer matches how risks emerge, how regulations change, or how fast decisions must be made. Traditional GRC tools were designed in an era when the primary goal was documentation and evidence: Keeping policy registers and tracking acknowledgements Maintaining risk registers and simple risk assessments Recording compliance checks and audit findings They are often module-based and process-centric, with risk, compliance, audit, and IT/security sitting in separate areas with limited integration. Each module may work reasonably well in isolation, but together they create siloed data models, heavy manual reconciliation, and governance that is inherently backward-looking. In short, traditional GRC tools are systems of record; a governance operating system must be a system of execution and intelligence. What a Governance Operating System Is A governance operating system is a connected platform that runs the core disciplines of governance as one integrated fabric, not as separate applications. At its heart is a single data model where risks, controls, obligations, policies, assets, vendors, incidents, issues, and actions all live in one shared structure. The same risk is not recreated in three different systems with three different scores. This model changes how work flows: A regulatory change automatically touches risks, controls, policies, testing, and training, with workflows following that end‑to‑end path rather than departmental boundaries. Dashboards, alerts, and analytics are driven by live data from ongoing activities—control tests, incidents, third‑party assessments, crisis events—not manually compiled slides. Intelligence is embedded into how risks are identified, obligations mapped, controls selected, and reports produced, rather than added later as a cosmetic layer. It represents a shift from recording what governance did to actually running governance as an operating layer of the organization. Why the Shift Is Now Inevitable The move from GRC tools to governance operating systems is being driven by structural pressures that are difficult to ignore. Regulatory complexity and overlap mean organizations now operate under multiple regulators and frameworks at once—central banks, financial services authorities, data protection laws, cyber frameworks, ESG expectations, and sector-specific rules. Mapping all of these into separate tools is not scalable. Risks are deeply interconnected. Cyber, third‑party, privacy, operational resilience, conduct, and financial reporting risks no longer live in neat boxes. A single incident can touch data, vendors, customers, and capital all at once. Fragmented tools cannot reflect these connections. Boards expect a single, clear view of top risks, control effectiveness, resilience posture, and regulatory exposure across entities and jurisdictions, without endless reconciliation. At the same time, risk, compliance, and audit teams cannot grow indefinitely; manual effort must give way to automated data flows, reusable libraries, and AI‑assisted work. When governance remains fragmented, the cost is not just inefficiency. Organizations face missed signals, slower response, and weaker confidence from both leadership and regulators. Design Principles of a Governance Operating System To address these pressures, a governance operating system needs to be designed differently from the ground up. A modern design typically follows a few key principles: Single source of truth Central libraries for risks, controls, obligations, policies, assets, vendors, KPIs, and the audit universe, so everyone works off the same definitions and scoring. End‑to‑end traceability The ability to trace a straight line from strategy and appetite through risks, controls, testing, incidents, issues, remediation, and assurance. Nothing is orphaned and nothing is duplicated. Execution‑first workflows The platform orchestrates tasks, approvals, evidence, and escalations. Dashboards reflect work actually happening in the system, not numbers manually pasted from elsewhere. AI‑native by design Intelligence is used to classify, map, summarise, and prioritise: suggesting risks, mapping regulatory clauses to controls, identifying anomalies in control performance, and drafting first‑cut reports. Human judgment is amplified, not replaced. Progressive adoption Organizations can start with a few high‑value use cases—such as regulatory obligations and enterprise risk—while keeping everything on one fabric so new capabilities plug into the same model rather than creating new silos. How Falconry360 Fits This New Model Falconry360 has been built explicitly as an AI-enabled governance operating system, not as a traditional GRC suite. Its architecture is organised into five integrated intelligence layers: GOVERN – strategy, ethics, culture, policies, and AI governance ANTICIPATE – enterprise, cyber, privacy, and third‑party risk, plus regulatory intelligence COMPLY – regulatory obligations, clause‑level mapping, regulatory change, and reporting WITHSTAND – operational resilience, business continuity, crisis and Minimum Viable Company (MVC) simulations ASSURE – internal audit, ICFR, combined assurance, and continuous monitoring All five layers run on a shared data model and central libraries. FalconryX, the embedded AI engine, sits across them, helping teams identify risks faster, map obligations more accurately, and convert raw data into decision-ready insights. For regulated organizations—especially in banking, financial services, public sector, and critical infrastructure—this means governance is no longer a patchwork of tools. It becomes a single operating layer aligned with regulatory expectations by design. What Changes for Boards and Executives When governance runs on an operating system instead of scattered tools, the impact at the top is tangible. Boards see a unified view of top risks, regulatory obligations, control